
Article · DAAKYI Perspectives
Managed SOC, MDR or MXDR: Choosing the Right Operating Model
DAAKYI Insights13 October 2026
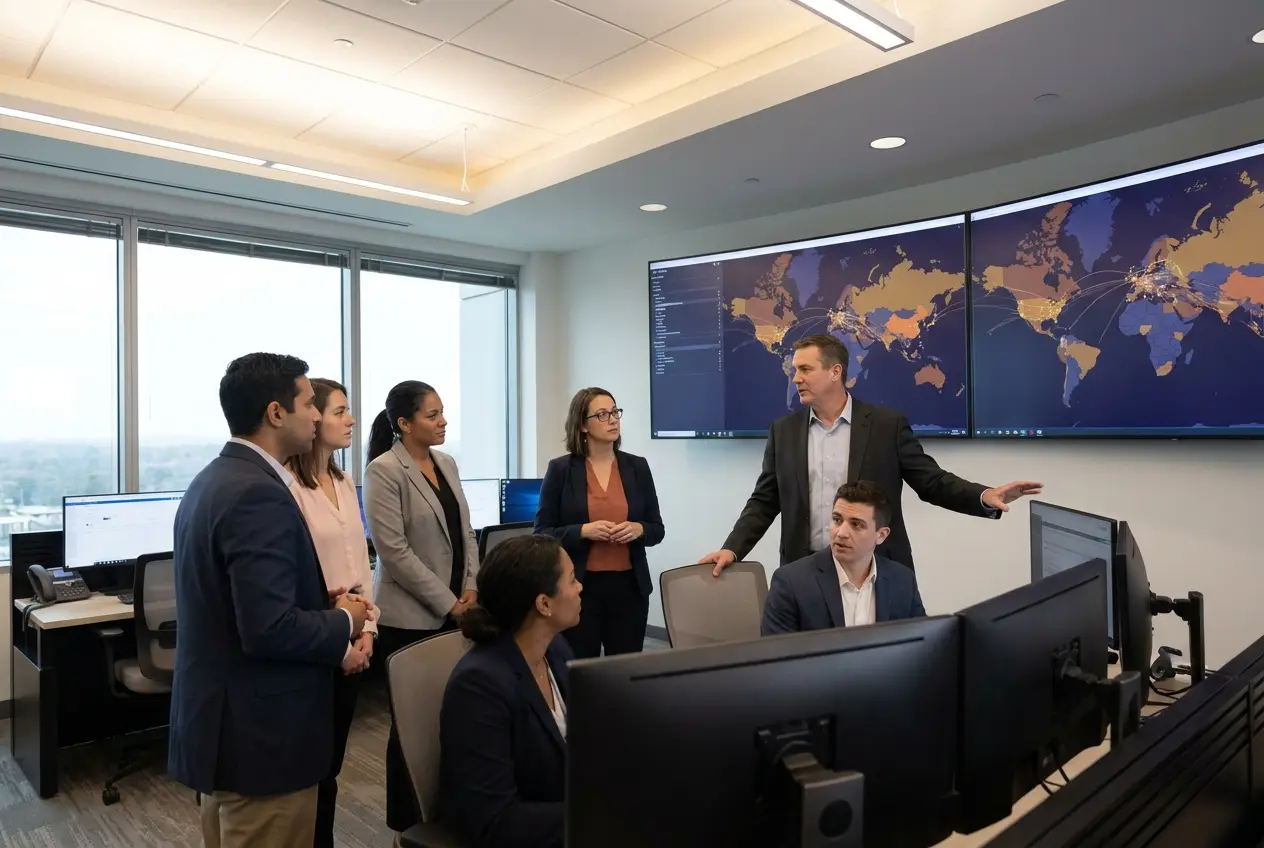
Three managed models, three levels of response. A practical guide to what each covers and which institutions each one suits.
Most institutions do not need to decide whether to monitor; they need to decide how far their managed service should go once something is detected. The difference between a managed SOC, managed detection and response (MDR) and managed XDR (MXDR) is the depth of response and the breadth of telemetry.
Managed SOC
24/7 monitoring, triage and escalation. Analysts watch correlated events, triage alerts and escalate confirmed incidents to your team with context. Suited to organizations with internal responders who need round-the-clock eyes.
The difference between a managed SOC, managed detection and response (MDR) and managed XDR (MXDR) is the depth of response and the breadth of telemetry.
Managed Detection & Response
Adds hunting, containment and remediation. Beyond alerting, the provider runs hypothesis-led threat hunts and takes agreed containment actions, shortening the time between detection and control.
Managed XDR
Unified response across endpoint, network, cloud and identity. Telemetry from every layer is correlated in one analytics core, so response is coordinated across the estate rather than tool by tool.
How the architecture fits together
- Telemetry: endpoints, network, cloud, identity, applications, OT and IoT.
- Collection: event collection with normalization, parsing and enrichment.
- Analytics core: SIEM and XDR correlation, threat intelligence, and detection engineering tuned to you.
- 24/7 SOC: L1 and L2 alert triage, hypothesis-led threat hunting, incident response with containment and forensics.
- Client outcomes: orchestrated response, case management, client dashboards and incident reporting.
Choosing a model
Start with your obligations and your internal capacity. If you need 24/7 coverage without building in-house, managed security services under SLAs are the natural fit. If ownership of the capability is the goal, a Build–Operate–Transfer model lets you begin managed and end sovereign.
Discuss This Perspective with a DAAKYI Specialist.
Talk to Our ExpertsRelated · DAAKYI Perspectives
 Article29 September 2026
DAAKYI Perspectives
CompaaS and the Case for Compliance Automation
Why compliance teams need structured controls and evidence rather than spreadsheets — and what CompaaS does.
Read- Article17 May 2026
DAAKYI Perspectives
Africa Will Not Win the AI Race Without Secure Infrastructure
Artificial Intelligence is no longer just a technology trend — it has become a national development priority, an economic competitiveness issue, and a foundation for the next generation of digital transformation. As African nations accelerate innovation, automate public services, modernize industries, and adopt AI-driven solutions, the ability to secure the infrastructure behind AI will determine…
Read - Article20 May 2023
DAAKYI Perspectives
Finding the Right Fit: What You Need to Know When Choosing a Managed Security Services Provider
Choosing the right cybersecurity provider is an important decision for any business or organization. With the increasing number of cyber attacks, it is essential to have the right protection in place. However, with so many options available, it can be difficult to know which provider is right for you. In this blog, we’ll explore the…
Read

