
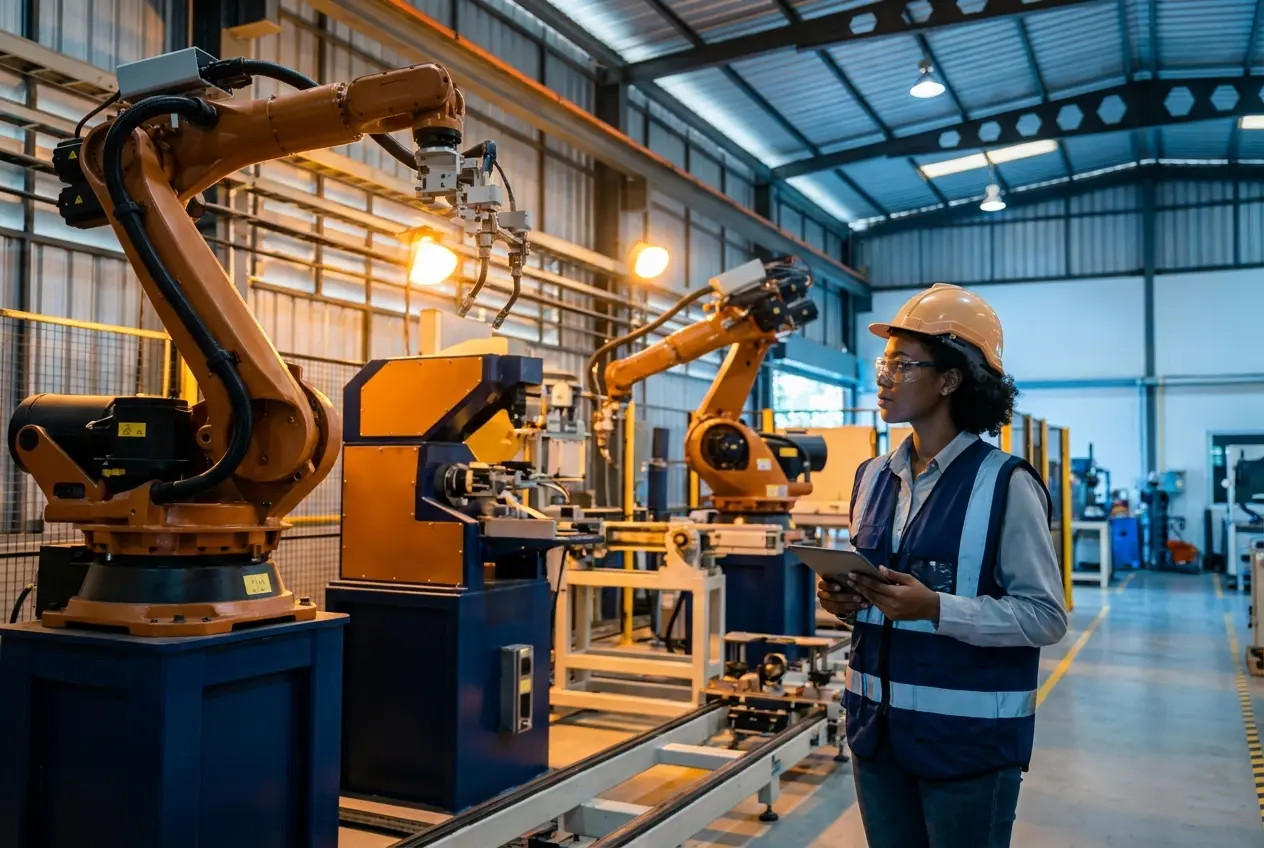
Manufacturing & Industrial
Protect Production Lines and the IP Behind Them.
Security for manufacturers where IT-to-OT pivoting, IP theft and production ransomware threaten output and quality.
Executive Summary
- 01Plant security fails at the seams: the links between office networks, controllers, vendors and the data that defines the product.
- 02Segmentation, remote-access control and plant-aware detection reduce the chance that a stolen credential becomes a stopped line.
- 03Recovery depends on offline copies of controller logic and recipes, tested before an incident rather than assumed.
MANUFACTURING · Risk Drivers
IT‑to‑OT pivoting, IP theft, production ransomware.
- Primary Attack Vectors
- IT-to-OT pivoting, IP theft, production ransomware
- Operational Consequences
- Production stoppage, safety and quality failures
In Depth
Security in Manufacturing & Industrial, Explained
Segment the Plant by Function
A plant network grows by accretion. A controller is added for a new line, a vendor laptop is plugged in for commissioning, and a flat network quietly forms. Segmentation reverses that drift. Engineers map assets into zones, such as enterprise IT, a demilitarized zone, supervisory systems, and cell-level controllers. They then define conduits, the only permitted paths between zones. Each conduit carries explicit rules on protocol, direction and endpoints. The goal is simple: a compromised office workstation should not be able to speak to a programmable logic controller. IEC 62443 uses this zone-and-conduit model as its core design pattern.
Detect Across Both Sides of the Boundary
Production ransomware rarely starts on the plant floor. It starts with a phished credential, an exposed remote service or a compromised supplier account, then moves toward systems that keep lines running. Detection therefore has to span both worlds. Endpoint and identity telemetry from IT shows credential theft, lateral movement and staging of data. Passive network monitoring in OT shows new devices, unexpected commands and changes to controller logic without touching fragile equipment. Analysts correlate the two views, so an odd login in the office can be tied to an unusual engineering session hours later. MITRE ATT&CK helps label the behavior consistently.
Treat Intellectual Property as Owned Data
Design files, recipes, tooling parameters and process settings are the intellectual property of a manufacturer. They sit in engineering workstations, product lifecycle systems, shared drives and supplier portals. Protection starts by finding and classifying them, then naming an owner for each class. Controls follow the classification: encryption at rest and in transit, tight access by role, logging of bulk copies, and restrictions on removable media and personal cloud storage. Supplier sharing needs special care. Files sent to contract partners should be watermarked or limited to the minimum required, and access should expire when the work ends. Departing staff and long-running contractors are frequent exposure points.
Ransomware seldom starts on the plant floor. It succeeds there when nothing stands between the office network and the controllers.
Threat Scenarios
What It Looks Like in Practice
Vendor Remote Access Abused
How It Shows Up
A maintenance account logs in outside the vendor's usual hours and opens sessions to several controllers.
Response
Brokered, time-limited access with session recording limits what a stolen vendor credential can reach, and out-of-pattern use triggers an alert.
Office Ransomware Heading for the Plant
How It Shows Up
Mass file encryption starts on office servers, then authentication attempts appear against historian and supervisory systems.
Response
Responders isolate affected segments, enforce conduit rules, and restore from offline backups of both IT systems and controller configurations.
Tampered Controller Logic
How It Shows Up
A controller program is downloaded outside a change window, or a project file differs from the approved baseline.
Response
Teams compare against golden configurations, investigate the engineering workstation involved, and tighten who may program controllers.
Design Files Leaving Through a Supplier or Insider
How It Shows Up
One account pulls large volumes of design files overnight and sends them to personal storage or an unmanaged partner address.
Response
Data-loss controls and logging flag the transfer, access is suspended, and classification shows which designs are exposed.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Vendor Remote Access Abused | A maintenance account logs in outside the vendor's usual hours and opens sessions to several controllers. | Brokered, time-limited access with session recording limits what a stolen vendor credential can reach, and out-of-pattern use triggers an alert. |
| Office Ransomware Heading for the Plant | Mass file encryption starts on office servers, then authentication attempts appear against historian and supervisory systems. | Responders isolate affected segments, enforce conduit rules, and restore from offline backups of both IT systems and controller configurations. |
| Tampered Controller Logic | A controller program is downloaded outside a change window, or a project file differs from the approved baseline. | Teams compare against golden configurations, investigate the engineering workstation involved, and tighten who may program controllers. |
| Design Files Leaving Through a Supplier or Insider | One account pulls large volumes of design files overnight and sends them to personal storage or an unmanaged partner address. | Data-loss controls and logging flag the transfer, access is suspended, and classification shows which designs are exposed. |
Regulatory & Operational Challenges
Plants mix modern IT with long‑lived OT and supplier connections.
A single ransomware event can stop production and trigger safety and quality failures.
Relevant DAAKYI Capabilities
Services for Manufacturing & Industrial
Delivery Approach
Priority Capabilities Across GUIDE, SECURE and OPERATE
GUIDE
OT and supply-chain assessment.
SECURE
Segmentation, endpoint, data protection.
OPERATE
MXDR, vulnerability remediation.
Methodology
The Method, Step by Step
- 1
Inventory and Map
Build a living inventory of IT and OT assets: controllers, drives, human-machine interfaces, historians, engineering stations and remote-access paths. Record firmware, protocols and who maintains each item. Passive discovery is used where active scanning could disturb equipment. The result is a map of how data and commands actually flow, which rarely matches the diagram on file.
- 2
Rank by Consequence
Score risk by what a failure would do to the plant, not only by technical severity. Ask which lines stop, which products fail quality checks, and where people could be harmed. Rank crown-jewel systems and crown-jewel data together. This puts a modest vulnerability on a bottleneck line above a severe one on an isolated test bench.
- 3
Contain and Harden
Apply segmentation, remote-access brokering, application allow-listing and multifactor authentication in order of consequence. Changes are scheduled around production windows and tested against a representative cell first. Where patching is impossible, compensating controls such as virtual segmentation or monitoring take its place and are documented as accepted exceptions.
- 4
Monitor and Rehearse
Connect plant telemetry to the same monitoring as enterprise systems and write playbooks that name plant operators as decision makers. Run tabletop exercises that include a stopped line, a manual-operations fallback and a call to a supplier. Rehearsal exposes gaps in authority long before an attacker does.
- 5
Recover and Improve
Keep offline, tested copies of controller programs, historian data, recipes and network device configurations. Measure how long a clean restart takes, then shorten it. After every incident or exercise, update asset records, segmentation rules and playbooks so lessons become controls instead of memories.
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| OT Asset and Data‑Flow Inventory | Gives engineers and security teams one trusted picture of what runs the plant and how it communicates. |
| Zone and Conduit Design | Defines which network segments exist and exactly which traffic may cross between them. |
| Consequence‑Ranked Risk Register | Orders remediation by effect on production, quality and safety. |
| Supplier Access Standard | Sets rules for vendor remote sessions, shared design files and access expiry. |
| Plant Incident Playbooks and Recovery Runbook | Tells operators and responders who decides what when a line is at risk, and how to restart cleanly. |
| Role | Responsibility |
|---|---|
| Plant or Operations Manager (Client) | Decides when containment actions may interrupt production and owns the manual-operations fallback. |
| Controls Engineer (Client) | Maintains controller programs and golden configurations and approves any change to the control network. |
| Security Lead or CISO (Client) | Owns risk acceptance for unpatchable systems and aligns plant security with enterprise policy. |
| OT Security Engineer (Provider) | Designs segmentation and monitoring that fit plant constraints and validates changes in a test cell first. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Unmapped
Assets are known only by the people who maintain them, networks are flat, and vendor access runs through permanent tunnels.
Stage 2
Visible
An inventory exists and passive monitoring shows traffic, but alerts are not yet tied to response actions.
Stage 3
Controlled
Zones and conduits are enforced, remote access is brokered, and exceptions for unpatchable systems are documented and reviewed.
Stage 4
Resilient
Plant and security teams rehearse together, restore from tested offline copies, and use incident lessons to change design.
Frameworks and Regulation
The Standards That Shape This Work
IEC 62443
This series addresses security for industrial automation and control systems. Its zone-and-conduit model guides segmentation, and its role-based parts help owners, integrators and suppliers share responsibility.
NIST SP 800-82
This guide covers OT security, including architecture, typical threats and controls adapted to the reliability and safety needs of control systems.
NIST CSF 2.0
Its six functions (Govern, Identify, Protect, Detect, Respond, Recover) give executives a common structure for plant and enterprise security reporting.
Ghana Cybersecurity Act, 2020 (Act 1038)
It provides for designation and protection of Critical Information Infrastructure and for incident reporting, which can matter for manufacturers whose operations are designated.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for engineers who have worked in plant environments and can explain how a change is tested before it touches a live line.
- Prefer assessments that use passive discovery in OT and state clearly where active scanning is excluded.
- Expect findings ranked by production and safety consequence, not by a raw vulnerability count.
- Require a recovery plan that covers controller logic, recipes and network configurations, not only servers.
Questions to ask a provider
- How do you avoid disturbing running equipment during discovery and testing?
- How will you handle systems that cannot be patched or restarted?
- Who on our plant team approves containment actions that could stop a line?
- How do you secure vendor remote access without blocking urgent maintenance?
Technical Detail
For Architects and Security Leads
Brokered Vendor Access to Controllers
Vendor remote access is a favored path into plants because it is built to reach controllers. A secure design removes direct VPN tunnels to the plant network. Vendors authenticate with multifactor credentials to a broker placed in the demilitarized zone, request a session for a named asset and period, and receive access only to that target. Sessions are recorded, and plant staff can watch or terminate them. Credentials for the equipment itself are held in a vault and never shown to the vendor. When the window closes, access ends automatically. Logs feed the monitoring platform, so an out-of-hours session raises an alert instead of passing unnoticed.
Passive Baselining and Logic Integrity
Passive monitoring connects to a switch mirror port or network tap and reads industrial protocol traffic without sending packets. Over a learning period it builds a baseline of which devices talk, which function codes they use and how often. Deviations then stand out: a new device on a control network, a write command from an engineering station that normally only reads, or a firmware download outside a change window. Pair this with periodic comparison of controller programs against golden configurations. Hash values of approved logic make unauthorized change visible. Alerts need plant context, so each one names the asset, its line and the safe first action.
Business Outcome
Continuous production and protected IP.
Glossary
Key Terms
- Conduit
- A controlled communication path between two network zones, with defined rules on what may cross.
- Historian
- A server that records time-series process data from the plant and often bridges OT and IT networks.
- Golden Configuration
- An approved, known-good copy of controller logic or device settings used to detect and reverse unauthorized change.
- Purdue Model
- A reference model that layers plant systems from the physical process up to enterprise IT to guide network separation.
FAQ
Questions Sector Leaders Ask

DAAKYI Intelligence
Ask Kasara About Manufacturing & Industrial
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.
Next Step