
GUIDE · Regulatory Assurance
Demonstrate Compliance to Every Regulator You Answer To.
We interpret national and sector obligations, map them to controls and help you evidence compliance across jurisdictions.
- Confidence before regulator reviews
- One obligation map across jurisdictions
- Evidence on demand
- 1Scope the Obligations
- 2Decompose Requirements
- 3Design the Controls
- 4Test and Rate Gaps
- 5Evidence and Report
Executive Summary
- 01Regulatory assurance turns legal text into controls that can be operated, tested and evidenced.
- 02One mapped control set can answer several regulators, which reduces duplicated work across countries.
- 03Compliance holds only when routine operations produce the evidence and the register is reviewed as laws change.
The Challenge
Regulated institutions answer to central banks, data protection authorities, sector regulators and national cybersecurity law at once.
Requirements overlap, change and are interpreted differently in each country of operation.
The DAAKYI Approach
DAAKYI translates each obligation into concrete controls, assesses your position and builds an assurance program with clear owners and evidence.
Multi-country operators get one map instead of parallel compliance efforts.
- 01
Obligation register by jurisdiction
- 02
Regulatory gap assessment
- 03
Assurance program and evidence plan
- 04
Regulator-ready reporting
In Depth
How the Discipline Works
From Statute to Testable Control
A regulation states an outcome. An auditor tests a control. Regulatory assurance bridges the two. Each obligation is broken into discrete requirements, such as register as a data controller, report incidents, protect critical information infrastructure, or safeguard cardholder data. Every requirement is then written as a control statement that someone can operate and someone else can test. The result is an obligation register where each line has a source, a jurisdiction, an interpretation approved by counsel, a control, an owner and an evidence type. Without this translation, teams argue about what a law means. With it, they argue only about whether the control works.
One Control, Many Obligations
Obligations overlap heavily. Incident reporting, access control, vendor oversight and data security appear in nearly every regime, worded differently each time. Mapping lets one well-designed control satisfy several obligations at once. The control is defined to the strictest applicable requirement, then tagged to each law it supports. Where a country adds a unique duty, such as registration with a data protection authority or accreditation of cybersecurity providers, it becomes a local extension rather than a separate program. This is how a multi-country operator avoids duplicated work, and how a change in one law is traced to the exact controls and evidence it affects.
Evidence That Stays Current
A control that worked last quarter proves nothing today. Evidence has to be generated by normal operations, not assembled before a review. Each control is paired with an artifact, a source system, a collection frequency and a named owner. Examples include access review records, vulnerability scan outputs, incident tickets with timestamps, training completion logs and vendor assessments. Reviewers can then sample from a current repository. Exceptions are logged with a justification and an expiry date. When a regulator asks a question, the answer is a retrieval task, not a project.
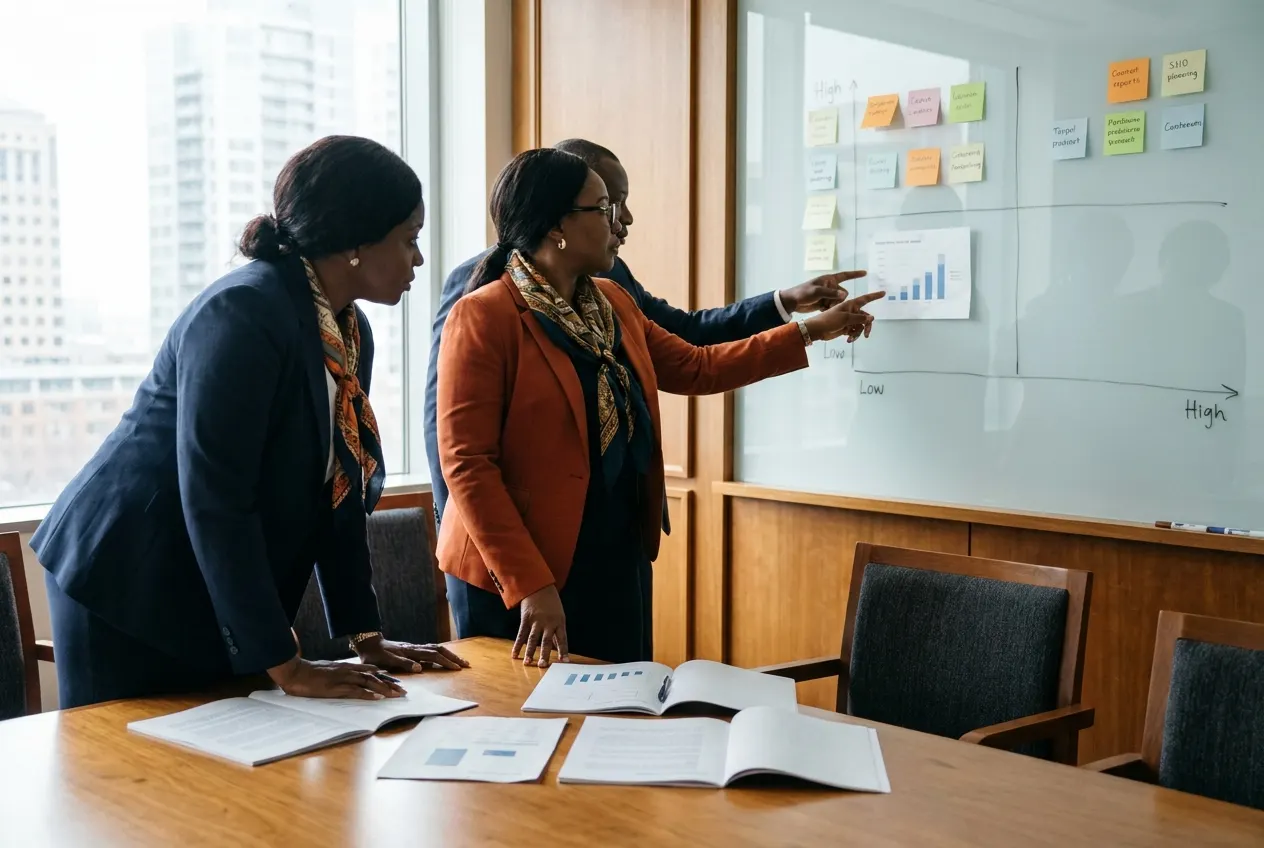
A regulator does not ask what you intended. It asks what you can show, today.
Capability Matrix
What the Service Includes
| Capability | Coverage | GUIDE | SECURE | OPERATE | Delivered Through |
|---|---|---|---|---|---|
| Regulatory Assurance Programs | Structured programs against named obligations. | GUIDE stage | – | – | Advisory Engagements |
| International Standards Enablement | Standards used to evidence regulatory controls. | GUIDE stage | – | – | Advisory Engagements |
| Cross‑Border Mapping | One view across countries of operation. | GUIDE stage | – | – | Advisory Engagements |
| Remediation Planning | Prioritized actions with owners. | GUIDE stage | – | – | Advisory Engagements |
Regulatory Assurance Programs
Structured programs against named obligations.
- Stage
- GUIDE
- Delivered Through
- Advisory Engagements
International Standards Enablement
Standards used to evidence regulatory controls.
- Stage
- GUIDE
- Delivered Through
- Advisory Engagements
Cross‑Border Mapping
One view across countries of operation.
- Stage
- GUIDE
- Delivered Through
- Advisory Engagements
Remediation Planning
Prioritized actions with owners.
- Stage
- GUIDE
- Delivered Through
- Advisory Engagements
How It Works
How Regulatory Assurance Works
- 01Obligations
- 02Map to Controls
- 03Assess
- 04Evidence
Methodology
The Method, Step by Step
- 1
Scope the Obligations
Identify every regulator, statute, directive and contractual standard that applies to each entity, product and country. Record the source text, effective dates and who the obligation binds. Confirm interpretation of ambiguous clauses with legal counsel. The output is a scoped list that everyone agrees is complete.
- 2
Decompose Requirements
Split each obligation into atomic requirements that can be answered yes or no. Remove duplicates across laws and note where one requirement is stricter than another. Assign a stable identifier to each so later changes in legislation can be traced to a specific line rather than a whole document.
- 3
Design the Controls
Write control statements that satisfy the strictest requirement in each cluster. Draw on recognized catalogs such as ISO/IEC 27001 Annex A or CIS Controls v8 for wording. Define the owner, the frequency and the test. Reuse existing controls where they already meet the bar, and note where they fall short.
- 4
Test and Rate Gaps
Assess each control for design and operating effectiveness using interviews, configuration review and sampled evidence. Rate each gap by regulatory exposure and likelihood of finding, not only technical severity. A missing registration or late reporting procedure can outweigh a technical weakness. Present results by obligation and by control.
- 5
Evidence and Report
Build the evidence plan, assign collectors and rehearse a regulator request. Prepare reports in the form each authority expects, drawn from the same repository. Review the register on a set cadence and whenever a law, directive or guidance changes, so the map never drifts from the text.
Operating Model
Delivered from the GUIDE Pillar
Pillar position
GUIDE
Advisory, Risk & Assurance
Engagement model
Advisory Engagements
Fixed-scope assessments, strategy, compliance and testing.
Best for · Defined questions with a clear deliverable
Threat Scenarios
What It Looks Like in Practice
Unannounced Regulator Information Request
How It Shows Up
A supervisor requests control evidence within days, and teams scramble across departments to assemble it.
Response
A maintained evidence repository and a rehearsed request process turn the demand into a retrieval exercise.
New or Amended Directive
How It Shows Up
A central bank or authority issues a directive that overlaps existing duties but adds new wording.
Response
The register is updated at requirement level, affected controls are identified, and only the real difference is remediated.
Breach with Several Notification Duties
How It Shows Up
One incident exposes personal data in multiple countries, each with its own authority and reporting clock.
Response
A notification matrix identifies recipients and deadlines at triage, so reporting runs alongside containment.
Divergent Interpretation Between Countries
How It Shows Up
Subsidiaries implement the same obligation differently, and group-level reporting cannot be reconciled.
Response
A group control defined to the strictest requirement is applied everywhere, with documented local extensions.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Unannounced Regulator Information Request | A supervisor requests control evidence within days, and teams scramble across departments to assemble it. | A maintained evidence repository and a rehearsed request process turn the demand into a retrieval exercise. |
| New or Amended Directive | A central bank or authority issues a directive that overlaps existing duties but adds new wording. | The register is updated at requirement level, affected controls are identified, and only the real difference is remediated. |
| Breach with Several Notification Duties | One incident exposes personal data in multiple countries, each with its own authority and reporting clock. | A notification matrix identifies recipients and deadlines at triage, so reporting runs alongside containment. |
| Divergent Interpretation Between Countries | Subsidiaries implement the same obligation differently, and group-level reporting cannot be reconciled. | A group control defined to the strictest requirement is applied everywhere, with documented local extensions. |
Outcomes
What Your Institution Gains
- Confidence before regulator reviews
- One obligation map across jurisdictions
- Evidence on demand
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Obligation Register | Lists every applicable requirement with its source, jurisdiction and approved interpretation. |
| Control Mapping Matrix | Shows which controls satisfy which requirements and where coverage is only partial. |
| Gap Assessment Report | Ranks shortfalls by regulatory exposure with recommended corrective actions. |
| Evidence Catalog | Defines the artifact, source, owner and frequency for each control. |
| Regulator Response Playbook | Sets out who answers a request, how evidence is retrieved and who approves the submission. |
| Role | Responsibility |
|---|---|
| Chief Compliance Officer (Client) | Owns the regulatory relationship and formally accepts any residual compliance risk. |
| Legal Counsel (Client) | Confirms the legal interpretation of each obligation on which the controls rely. |
| Control Owner (Client) | Operates a mapped control and supplies its evidence on the agreed schedule. |
| Assurance Lead (Provider) | Maintains the register, runs the assessment and reports gaps by obligation. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Reactive
Compliance is assembled for each audit from spreadsheets and email. Each country works alone.
Stage 2
Defined
Obligations are listed and controls assigned, but mapping is partial and evidence is collected by hand.
Stage 3
Managed
One map covers all jurisdictions, owners test controls on schedule and evidence is current.
Stage 4
Continuous
Regulatory changes flow into the register through a standing process, and control health is monitored continuously.
Frameworks and Regulation
The Standards That Shape This Work
ISO/IEC 27001:2022
Annex A contains 93 controls grouped into four themes: organizational, people, physical, and technological. Together they form a recognized control set to which many regulatory requirements can be mapped, and ISO/IEC 27002 provides guidance on applying them.
NIST CSF 2.0
The framework's six functions are Govern, Identify, Protect, Detect, Respond, and Recover. Together, they give organizations a common structure for presenting control coverage to executives and supervisors.
PCI DSS v4.0.1
This is the current revision of v4.0, whose future-dated requirements became mandatory on 31 March 2025. Cardholder data environments should be assessed against the full set.
Ghana Act 1038 and Act 843
Act 1038 provides for the designation of Critical Information Infrastructure, the accreditation of cybersecurity providers, and incident reporting. Under Act 843, data controllers must register, and the law establishes eight privacy principles.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for a provider that maps obligations to controls at requirement level, not a document-level checklist.
- Look for a clear boundary between security interpretation and legal advice, with counsel kept in the loop.
- Look for experience with the specific regulators and statutes you answer to in each country.
- Look for deliverables your own team can maintain after the engagement ends.
Questions to ask a provider
- How do you handle conflicting requirements between two jurisdictions?
- How will we trace a legislative change to the controls it affects?
- What evidence would be ready if a regulator called next week?
- Which parts of the register can our team maintain without you?
Regulatory & Industry Context
The Obligations This Service Supports
Typical obligations include Ghana's Act 1038 and Act 843, UAE NESA, the Nigeria Data Protection Act, PCI DSS and GDPR for cross-border data.
Frameworks DAAKYI helps clients implement
- Ghana Act 1038
- Ghana Act 843
- UAE NESA
- Nigeria Data Protection Act
- PCI DSS
- GDPR
Framework references describe client implementation support, not DAAKYI certifications.
Technical Detail
For Architects and Security Leads
Telemetry sources and partner technologies
Technology partners DAAKYI works with in this area.
Framework and regulatory alignment
- Ghana Act 1038
- Ghana Act 843
- UAE NESA
- Nigeria Data Protection Act
- PCI DSS
- GDPR
Typical obligations include Ghana's Act 1038 and Act 843, UAE NESA, the Nigeria Data Protection Act, PCI DSS and GDPR for cross-border data.
Architecture reference
How Regulatory Assurance Works: Obligations → Map to Controls → Assess → Evidence.
DAAKYI translates each obligation into concrete controls, assesses your position and builds an assurance program with clear owners and evidence.
Control-to-Obligation Traceability Model
The core data structure is a many-to-many matrix. Rows are atomic requirements with identifier, source citation, jurisdiction, effective date and binding entity. Columns are controls with owner, test procedure, frequency and evidence artifact. A cell records coverage as full, partial or none, plus the rationale. Because mapping is many-to-many, one access review control may cover requirements in several laws, and a gap in it surfaces everywhere it is used. Version every row so a legislative amendment creates a new record instead of overwriting the old one. Export views by regulator, by entity or by standard, so a central bank examination and a data protection audit draw on the same underlying records.
Incident Reporting Clocks and Thresholds
Reporting duties are time-bound and trigger-based, so they need engineering, not just policy. GDPR, for example, requires notifying the supervisory authority of a personal-data breach within 72 hours where feasible, unless the breach is unlikely to result in risk. Other regimes set their own triggers, recipients and content. Build a single notification matrix listing each regime, the trigger test, the clock start, the recipient and the approver. Wire it into the incident process aligned with NIST SP 800-61, so severity triage includes a regulatory question at the first decision point. Record when awareness occurred, since clocks may start there. Rehearse with a tabletop that includes counsel and the data protection officer.
Glossary
Key Terms
- Control Mapping
- The documented link between a regulatory requirement and the control that satisfies it.
- Operating Effectiveness
- Evidence that a control worked consistently over a period, not merely that it exists.
- Evidence Artifact
- A record, such as a log, approval or report, that proves a control operated.
- Regulatory Delta
- The difference between an amended obligation and the controls already in place.
Related
Explore Connected Capabilities
Related services
Platforms
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
Technology partners
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About Regulatory Assurance
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.

Next Step
Discuss Regulatory Assurance with DAAKYI
Tell us about your environment and obligations. A DAAKYI specialist for Regulatory Assurance will respond.
Talk to a Cybersecurity Expert