
SECURE · DevSecOps and Secure Code Review
Security That Moves at the Speed of Delivery.
We integrate security testing and code review into your pipelines so secure releases become the default.
- Fewer vulnerabilities reaching production
- Security without slowing releases
- Developers who write safer code
- 1Map the Delivery Pipeline
- 2Model Threats
- 3Tune and Enforce
- 4Review Critical Code
- 5Measure and Retrain
Executive Summary
- 01Security defects cost least to fix at commit time, so checks belong in the pipeline rather than at the end of the release.
- 02Automated tools find known patterns, while manual review of high-risk code finds flawed business logic.
- 03Progress is measured by which weakness classes stop recurring, not by how many findings are logged.
The Challenge
Release cycles have shortened, but security review still happens at the end, if at all.
Developers receive findings too late and without context, so the same flaws keep returning.
The DAAKYI Approach
DAAKYI evaluates your pipeline, integrates automated security checks and performs secure code review on high‑risk components.
Developers get coaching and guardrails rather than gates alone.
- 01
DevSecOps maturity evaluation
- 02
Pipeline security integration
- 03
Secure code review
- 04
Developer enablement
In Depth
How the Discipline Works
Why Findings Arrive Late
Most security defects are cheap to fix when the author still remembers the change and expensive once the code ships. DevSecOps moves detection to the point of commit. Checks run on the pull request, the build, and the deployment, so a developer sees a finding within the same working session. The finding names the file, the line, the weakness class, and a recommended fix. That context is what stops repeat flaws. A report delivered weeks later cannot do this. It arrives after the team has moved on, and it reads like an audit instead of feedback.
What Automated Checks Cover
A pipeline combines several automated techniques, each with a different blind spot. Static analysis reads source for unsafe patterns. Software composition analysis checks third-party libraries against known vulnerabilities and license terms. Secret scanning catches credentials committed to repositories. Infrastructure-as-code scanning flags insecure cloud and container definitions before they are applied. Dynamic testing probes a running build for flaws that only appear at runtime. No single tool is enough. The value comes from combining them, tuning rules to the codebase, and suppressing noise so developers trust what remains.
Where Manual Review Still Wins
Tools find patterns. People find intent. Manual secure code review examines authentication, authorization, session handling, cryptography use, payment logic, and input handling in the components where compromise would hurt most. Reviewers trace data from entry point to sink and test business rules the scanner cannot understand, such as whether one customer can read another customer's record. Review effort is concentrated by risk, using threat modeling to choose targets. The outcome is a short list of validated findings with exploit reasoning, not a long list of unverified alerts.
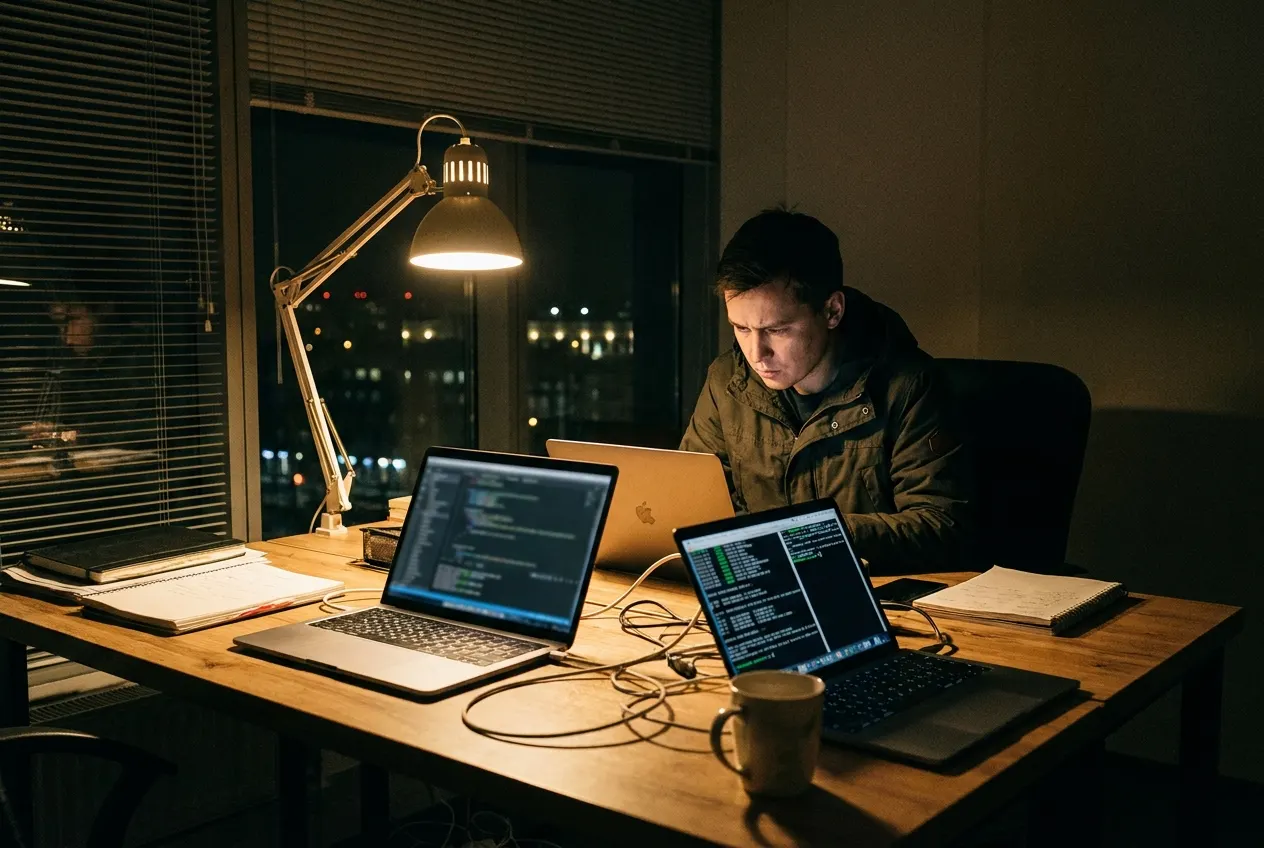
A finding a developer sees before merge is a lesson; a finding seen after release is an incident report.
Capability Matrix
What the Service Includes
| Capability | Coverage | GUIDE | SECURE | OPERATE | Delivered Through |
|---|---|---|---|---|---|
| DevSecOps Evaluation | Pipeline maturity and gaps. | – | SECURE stage | – | Project Implementation, Capability Development |
| DevSecOps Integration | Automated checks in CI/CD. | – | SECURE stage | – | Project Implementation, Capability Development |
| Secure Code Review | Manual review of critical code. | – | SECURE stage | – | Project Implementation, Capability Development |
| Secure Software Development | Practices and developer guidance. | – | SECURE stage | – | Project Implementation, Capability Development |
DevSecOps Evaluation
Pipeline maturity and gaps.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Capability Development
DevSecOps Integration
Automated checks in CI/CD.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Capability Development
Secure Code Review
Manual review of critical code.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Capability Development
Secure Software Development
Practices and developer guidance.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Capability Development
How It Works
How DevSecOps and Secure Code Review Works
- 01Evaluate
- 02Integrate
- 03Review
- 04Enable
Methodology
The Method, Step by Step
- 1
Map the Delivery Pipeline
Inventory repositories, build systems, artifact registries, deployment targets, and who can change each. Record where code, secrets, and dependencies enter, and where approvals are enforced or skipped. This map shows which stages can host checks, which are unprotected, and which components carry the most business and regulatory risk.
- 2
Model Threats
For each high-risk application, sketch trust boundaries, data flows, and likely attackers. List abuse cases such as account takeover, payment tampering, and data exposure through APIs. These cases set the review scope and shape which rules the automated tools must enforce, so effort follows realistic attack paths rather than tool defaults.
- 3
Tune and Enforce
Introduce checks in monitoring mode first and measure false positives. Then set policy: which severities fail a build, which open a tracked ticket, and which are accepted with an owner and expiry date. Enforcement begins only when developers agree the signal is reliable, which protects both release speed and credibility.
- 4
Review Critical Code
Reviewers read the highest-risk components line by line, guided by the threat model and by secure coding standards such as OWASP ASVS. Each finding is reproduced or reasoned through, rated by exploitability and impact, and paired with a specific remediation. Developers walk through results with reviewers, not just receive a document.
- 5
Measure and Retrain
Track recurring weakness classes, time to fix, and escape rate to production. Feed the top patterns back into coding guidance, templates, and training. If injection flaws keep returning, the answer is a safer library and a lint rule, not another reminder. Improvement is judged by what stops reappearing.
Operating Model
Delivered from the SECURE Pillar
Pillar position
SECURE
Engineering, Architecture & Implementation
Engagement model
Project Implementation
Design and deployment of security technologies.
Best for · Modernization and transformation
Engagement model
Capability Development
Training, certification and mentoring programs.
Best for · Regulators and operators growing talent
Threat Scenarios
What It Looks Like in Practice
Hardcoded Credentials in a Repository
How It Shows Up
An API key or database password sits in source history, often copied into forks and build logs.
Response
Secret scanning blocks the commit, the exposed credential is rotated, and secrets move to a managed vault.
Vulnerable Open‑Source Dependency
How It Shows Up
A widely used library is disclosed as exploitable, and nobody knows which services include it.
Response
Composition analysis and release-level bills of materials identify affected builds fast, and fixes are prioritized by exposure.
Broken Authorization in an API
How It Shows Up
A user changes an identifier in a request and receives another user's data. Scanners report nothing.
Response
Manual review traces access checks on every object path, and the fix is paired with a regression test.
Misconfigured Cloud Template
How It Shows Up
A deployment template opens a storage bucket or management port to the internet.
Response
Infrastructure-as-code scanning fails the build before deployment and points to the safe configuration.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Hardcoded Credentials in a Repository | An API key or database password sits in source history, often copied into forks and build logs. | Secret scanning blocks the commit, the exposed credential is rotated, and secrets move to a managed vault. |
| Vulnerable Open‑Source Dependency | A widely used library is disclosed as exploitable, and nobody knows which services include it. | Composition analysis and release-level bills of materials identify affected builds fast, and fixes are prioritized by exposure. |
| Broken Authorization in an API | A user changes an identifier in a request and receives another user's data. Scanners report nothing. | Manual review traces access checks on every object path, and the fix is paired with a regression test. |
| Misconfigured Cloud Template | A deployment template opens a storage bucket or management port to the internet. | Infrastructure-as-code scanning fails the build before deployment and points to the safe configuration. |
Outcomes
What Your Institution Gains
- Fewer vulnerabilities reaching production
- Security without slowing releases
- Developers who write safer code
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Pipeline Threat Map | Shows where code, secrets, and dependencies enter and which stages lack controls. |
| Check and Policy Configuration | Defines which findings block a build, which are tracked, and who owns exceptions. |
| Secure Code Review Report | Lists validated findings with severity, exploit reasoning, and specific fixes. |
| Secure Coding Guidance | Gives developers language-specific patterns that remove recurring weakness classes. |
| Remediation Tracking Summary | Shows fix progress and recurring defect trends for engineering and risk leaders. |
| Role | Responsibility |
|---|---|
| Engineering Lead (Client) | Owns pipeline changes and agrees which findings fail a build. |
| Application Owner (Client) | Accepts or remediates risk for each finding and signs off exceptions. |
| Secure Code Reviewer (Provider) | Performs manual review of critical components and validates every reported finding. |
| DevSecOps Engineer (Provider) | Integrates and tunes scanning tools so results are accurate and fast. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Ad Hoc
Security testing happens before major releases, if at all, and findings arrive as documents with little context.
Stage 2
Automated
Scanners run in the pipeline, but rules are untuned, alerts are noisy, and developers often ignore them.
Stage 3
Enforced
Policy blocks high-severity issues, exceptions have owners and expiry dates, and manual review targets risky components.
Stage 4
Optimized
Defect trends drive coding standards, secure templates, and training, and recurring weaknesses steadily disappear.
Frameworks and Regulation
The Standards That Shape This Work
ISO/IEC 27001:2022 Annex A
The technological theme includes controls for secure coding, security testing in development, and secure development life cycles. ISO/IEC 27002:2022 gives implementation guidance.
PCI DSS v4.0 and v4.0.1
Teams that handle payment data must meet requirements for developing and maintaining secure software. The standard's future-dated requirements became mandatory on March 31, 2025.
OWASP Top 10 and ASVS
The Top 10 names common web application risks, while ASVS provides verifiable requirements that reviewers can test code against.
Buyer Guidance
Choosing the Right Provider
What to look for
- Reviewers who can read your languages and frameworks, not only operate scanning tools.
- A tuning plan that measures false positives before any check is allowed to block releases.
- Findings that include exploit reasoning and a concrete fix, not only a scanner export.
- Attention to the pipeline's own security, including runners, secrets, and approval rules.
Questions to ask a provider
- How do you decide which components receive manual review?
- How do you reduce false positives before enforcing a gate?
- How are exceptions recorded, owned, and expired?
- How will you show that recurring weaknesses are declining?
Regulatory & Industry Context
The Obligations This Service Supports
Practices support ISO/IEC 27001 secure development controls and PCI DSS software security requirements.
Frameworks DAAKYI helps clients implement
- ISO/IEC 27001
- PCI DSS
- SOC 2
Framework references describe client implementation support, not DAAKYI certifications.
Technical Detail
For Architects and Security Leads
Framework and regulatory alignment
- ISO/IEC 27001
- PCI DSS
- SOC 2
Practices support ISO/IEC 27001 secure development controls and PCI DSS software security requirements.
Architecture reference
How DevSecOps and Secure Code Review Works: Evaluate → Integrate → Review → Enable.
DAAKYI evaluates your pipeline, integrates automated security checks and performs secure code review on high-risk components.
Tuning Static Analysis for Signal
Out-of-the-box static analysis rule sets produce volume, and volume trains developers to ignore results. Tuning starts with the language and framework in use, enabling rules that understand its sanitizers and routing conventions. Teams then baseline existing findings so only new issues block a merge. Custom rules encode house patterns, such as an approved encryption wrapper or a mandatory authorization decorator. Taint analysis, which follows untrusted input to sensitive sinks, deserves particular attention for injection and deserialization flaws. Each rule should carry a severity, a rationale, and a remediation example. Review the rule set on a schedule, retiring rules that generate dismissals and adding rules from confirmed manual review findings.
Securing the Build and Supply Chain
The pipeline itself is a target. An attacker who controls a build runner or a dependency can ship malicious code that every scanner approves. Harden it by running builds on ephemeral, isolated runners with least-privilege credentials, and by storing secrets in a vault rather than in pipeline variables. Pin dependency versions and verify checksums. Generate a software bill of materials for each release so affected components can be found quickly when a new vulnerability is disclosed. Sign artifacts and verify signatures at deploy time. Require reviewed approvals for changes to pipeline definitions, because those files control everything downstream.
Glossary
Key Terms
- SAST
- Static application security testing analyzes source code for vulnerabilities without running it.
- SCA
- Software composition analysis identifies known vulnerabilities and license issues in third-party components.
- Taint Analysis
- A technique that follows untrusted input through code to see whether it reaches a sensitive operation unchecked.
- SBOM
- A software bill of materials lists the components inside a release so affected builds can be found quickly.
Related
Explore Connected Capabilities
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About DevSecOps and Secure Code Review
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.

Next Step
Discuss DevSecOps and Secure Code Review with DAAKYI
Tell us about your environment and obligations. A DAAKYI specialist for DevSecOps and Secure Code Review will respond.
Talk to a Cybersecurity Expert