
Solution · Cyber Incident Readiness & Recovery
Be Ready Before the Incident, and Recover Cleanly After It.
The Challenge
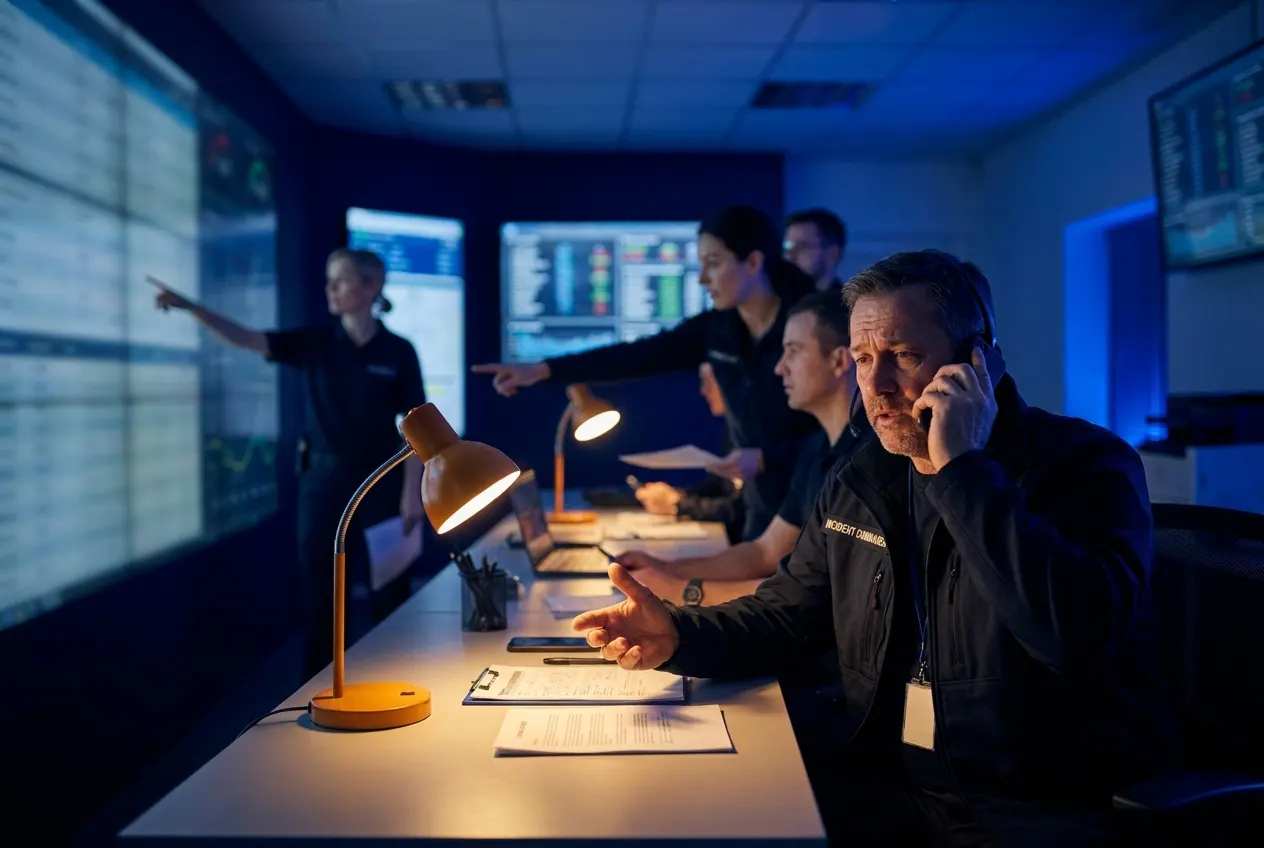
When ransomware or extortion strikes, unprepared organizations lose days deciding who leads and what to restore first.
The Outcome
- Rehearsed, proven recovery
- Forensic, regulator-ready evidence
- Leaders who have rehearsed their response
Executive Summary
- 01Authority, not tooling, decides how fast an organization contains an incident.
- 02Backups only count when a full restoration has been rehearsed against agreed recovery targets.
- 03Evidence collected in the first hours determines what regulators, insurers, and courts will accept.
The Challenge
When ransomware or extortion strikes, unprepared organizations lose days deciding who leads and what to restore first.
Untested backups and missing evidence turn an incident into a regulatory and reputational event.
The DAAKYI Approach
DAAKYI prepares playbooks and decision rights, rehearses them with executives and responders, and stands behind them with DFIR and recovery operations.
After every incident or exercise, lessons feed back into the plan.
Delivered Through These DAAKYI Services
Relevant industries
- 01
Playbooks and decision rights
- 02
Executive and technical exercises
- 03
Forensic incident response
- 04
Clean, tested recovery
In Depth
How the Solution Comes Together
Decision Rights Come Before Tooling
An incident response plan fails when it describes technology but not authority. Readiness starts by naming who can isolate a production system, who approves a ransom-related decision, who speaks to regulators, and who informs staff and customers. Those decision rights are written into playbooks for specific scenarios such as ransomware, business email compromise, and data theft. Each playbook lists triggers, first actions, escalation paths, and evidence handling rules. Because the roles are agreed in advance, the first hours go to containment and not to debate. Playbooks are short enough to use under stress and are reviewed whenever systems or leadership change.
Exercises Expose Gaps Cheaply
A tabletop exercise walks leaders through an unfolding incident using injected facts: a ransom note, a journalist inquiry, a regulator call, a supplier outage. Executives practice decisions on shutdown, customer notice, and payment policy without touching live systems. A parallel technical exercise tests responders on log access, isolation steps, and restoration procedures. Observers record where decisions stalled, where contacts were missing, and where the playbook was silent. Findings become assigned actions with owners and dates. Repeating the exercise after fixes shows whether the gaps actually closed, which is the only reliable measure of improvement.
Recovery Is Proven, Not Assumed
Backups count only if they restore. Recovery planning ranks systems by business impact, sets the order of restoration, and identifies dependencies such as identity services, DNS, and databases that other systems need first. Backup copies should be isolated from the production domain so an intruder with administrator rights cannot delete them. Restoration is rehearsed in a clean environment, and results are compared against the recovery time and recovery point each business owner expects. Before systems return to service, responders confirm the intruder's access is removed, credentials are reset, and monitoring is in place to catch re-entry.
The first hours of an incident should be spent containing it, not deciding who is allowed to.
Capability Matrix
What the Service Includes
Incident Playbooks
Roles and actions agreed in advance.
Tabletop Exercises
Leaders rehearse realistic scenarios.
DFIR
Containment and regulator-ready evidence.
Cyber Recovery
Systems restored clean.
Operating Model
Delivered from the GUIDE · SECURE · OPERATE Pillar
Pillar position
GUIDE · SECURE · OPERATE
Delivered across all three pillars
Engagement model
Advisory Engagements
Fixed-scope assessments, strategy, compliance and testing.
Best for · Defined questions with a clear deliverable
Engagement model
Managed Security Services
SOC, MXDR and managed cloud security under SLAs.
Best for · 24/7 coverage without building in-house
Threat Scenarios
What It Looks Like in Practice
Ransomware with Backup Deletion
How It Shows Up
Administrator accounts log in at odd hours, backup jobs fail, and then file servers encrypt.
Response
Isolate affected segments, protect surviving backup copies, and restore in the agreed priority order after confirming the intruder is removed.
Extortion Without Encryption
How It Shows Up
A message claims stolen data and sets a deadline, while systems still run normally.
Response
Verify the claim through forensic analysis of outbound traffic, then follow the playbook's legal, communication, and notification steps.
Business Email Compromise
How It Shows Up
A supplier's bank details change by email, or forwarding rules appear in an executive mailbox.
Response
Revoke sessions, remove malicious rules, review mailbox audit logs, and alert the bank to attempt a payment recall.
Cloud Account Takeover
How It Shows Up
Unfamiliar API calls, new access keys, and unexpected compute resources appear in the cloud tenant.
Response
Disable compromised identities, rotate keys, preserve cloud audit logs, and rebuild affected workloads from trusted templates.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Ransomware with Backup Deletion | Administrator accounts log in at odd hours, backup jobs fail, and then file servers encrypt. | Isolate affected segments, protect surviving backup copies, and restore in the agreed priority order after confirming the intruder is removed. |
| Extortion Without Encryption | A message claims stolen data and sets a deadline, while systems still run normally. | Verify the claim through forensic analysis of outbound traffic, then follow the playbook's legal, communication, and notification steps. |
| Business Email Compromise | A supplier's bank details change by email, or forwarding rules appear in an executive mailbox. | Revoke sessions, remove malicious rules, review mailbox audit logs, and alert the bank to attempt a payment recall. |
| Cloud Account Takeover | Unfamiliar API calls, new access keys, and unexpected compute resources appear in the cloud tenant. | Disable compromised identities, rotate keys, preserve cloud audit logs, and rebuild affected workloads from trusted templates. |
Outcomes
What Your Institution Gains
- Rehearsed, proven recovery
- Forensic, regulator-ready evidence
- Leaders who have rehearsed their response
Methodology
The Method, Step by Step
- 1
Scope Critical Services
List the services whose loss would stop revenue, care, or public duties. Assign each an owner, a tolerable outage, and a tolerable data loss. These values drive backup design, restoration order, and the scenarios chosen for exercises, so they must come from business owners, not from IT alone.
- 2
Write Scenario Playbooks
Draft scenario playbooks covering ransomware, extortion, account takeover, and insider misuse. Each defines triggers, severity levels, decision makers, notification duties, and evidence preservation steps. Keep them short and role-based so a responder at night can follow them without searching a long document.
- 3
Run Realistic Exercises
Rehearse the playbooks with executives and technical responders separately, then together. Use realistic injects, time pressure, and incomplete information. Record decisions, delays, and missing contacts. Score the results against the playbook so that every gap becomes a tracked action rather than a passing comment.
- 4
Investigate and Contain
During a live incident, responders scope the intrusion, preserve volatile and disk evidence, and contain spread without destroying proof. Timelines of attacker activity are built from logs and artifacts. Findings support regulator notices, insurer claims, and any legal action, so chain of custody is documented from the first acquisition.
- 5
Restore and Learn
Rebuild or restore systems in the agreed order, validate integrity, reset credentials, and watch for re-entry before declaring recovery. Then hold a structured review. Update playbooks, contact lists, and controls with what was learned, and schedule the next exercise to test the changes.
How It Works
How Cyber Incident Readiness & Recovery Comes Together
- 01Prepare
- 02Rehearse
- 03Respond
- 04Recover
Regulatory & Industry Context
The Obligations This Service Supports
Supports incident reporting under Act 1038, breach notification under Act 843 and GDPR, and ISO/IEC 22301.
Frameworks DAAKYI helps clients implement
- Ghana Act 1038
- Ghana Act 843
- GDPR
- ISO/IEC 22301
Framework references describe client implementation support, not DAAKYI certifications.
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Scenario Playbooks | Give responders and leaders step-by-step actions for each defined incident type. |
| Decision Rights Matrix | Records who may authorize shutdown, notification, and external communication. |
| Exercise Report | Documents decisions, gaps, and assigned corrective actions after each rehearsal. |
| Forensic Findings Report | Sets out the timeline, scope, and evidence that regulators and insurers may request. |
| Recovery Test Record | Shows measured restoration results against agreed recovery time and recovery point targets. |
| Role | Responsibility |
|---|---|
| Executive Incident Lead (Client) | Makes business decisions on shutdown, disclosure, and spending during the incident. |
| Legal and Privacy Counsel (Client) | Determines notification duties and manages privileged communication with regulators. |
| Forensic Responder (Provider) | Collects evidence, scopes the intrusion, and advises on containment steps. |
| Recovery Engineer (Provider) | Rebuilds and restores systems in priority order and validates their integrity. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Ad Hoc
No written playbook exists. Response depends on whoever is available and on personal contacts.
Stage 2
Documented
Plans and contact lists exist but have not been exercised, and backups have not been fully restored.
Stage 3
Rehearsed
Executives and responders run exercises regularly, and restoration is tested against recovery targets.
Stage 4
Adaptive
Lessons from incidents and exercises update playbooks and controls, and results are reported to the board.
Frameworks and Regulation
The Standards That Shape This Work
NIST SP 800-61
Provides a recognized lifecycle for incident handling, from preparation through detection, containment, recovery, and post-incident review.
NIST CSF 2.0
The framework centers on six functions: Govern, Identify, Protect, Detect, Respond, and Recover. Respond and Recover map directly to this discipline, while Govern frames decision rights.
ISO 22301
Specifies requirements for a business continuity management system, supporting impact analysis, recovery objectives, and exercising of plans.
GDPR
Requires notifying the supervisory authority of a personal-data breach within 72 hours where feasible, unless it is unlikely to result in risk, so playbooks need an early assessment step.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for a provider that preserves evidence before it restores systems.
- Look for exercises that include executives, legal, and communications, not only the IT team.
- Look for recovery testing that restores full applications and measures the time taken.
- Look for deliverables that map to the notification duties in the laws that apply to you.
Questions to ask a provider
- How do you preserve volatile evidence and document chain of custody?
- Can you show a sample exercise report with assigned actions?
- How do you verify the intruder is removed before systems return to service?
- Which regulatory notification duties do you build into your playbooks?
Technical Detail
For Architects and Security Leads
Backup Architecture for Ransomware Resilience
Ransomware operators target backups early. They seek domain administrator rights, enumerate backup servers, and delete or encrypt repositories before triggering encryption. Resilient design keeps at least one copy immutable or offline, uses separate credentials and no shared domain trust for the backup platform, and requires multi-person approval to delete restore points. Backup consoles sit behind strong authentication on an isolated management network. Restore tests should cover a full application stack, not single files, and should measure how long identity, database, and application tiers take to return in sequence. Test restores also scan recovered data for malware so reinfection is not carried back into production.
Evidence Handling and Forensic Timelines
Forensic value depends on what is preserved in the first hours. Responders capture memory from affected hosts before reboot, acquire disk images with verified hashes, and export authentication, endpoint, firewall, and cloud audit logs before retention windows expire. Volatile data vanishes at shutdown, so order of collection matters. Each item enters a custody log recording who collected it, when, and how. Analysts map observed behavior to MITRE ATT&CK tactics to reconstruct initial access, privilege escalation, lateral movement, and exfiltration. The resulting timeline answers the questions regulators ask: what data was reached, when the intruder arrived, and whether access is truly closed.
Glossary
Key Terms
- RTO
- Recovery time objective is the longest outage a business service can tolerate before restoration.
- RPO
- Recovery point objective is the maximum data loss, measured in time, that the business can accept.
- Chain of Custody
- The documented record of who handled each piece of evidence, when, and why.
- Immutable Backup
- A backup copy that cannot be altered or deleted during its retention period.
Related
Explore Connected Capabilities
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About Cyber Incident Readiness & Recovery
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.
Next Step
Discuss Cyber Incident Readiness & Recovery with DAAKYI
Tell us the outcome you need; a DAAKYI specialist will map it to the right services and engagement model.