
SECURE · Security Technology Integration
Make Your Security Tools Work as One System.
We design, deploy and integrate partner technologies so controls share data, workflows and reporting.
- Controls integrated end to end
- More value from existing licences
- Every deployment tested
- 1Inventory and Map
- 2Design Data Flows
- 3Build and Configure
- 4Test End to End
- 5Document and Hand Over
Executive Summary
- 01Integration turns separate security products into one system by defining what each tool sends, receives and enforces.
- 02Normalized telemetry and tested connectors decide whether analysts see one timeline or several disconnected dashboards.
- 03Integrations are privileged paths, so they need their own credentials, health monitoring, documentation and change control.
The Challenge
Many estates run dozens of security tools that do not exchange data, leaving analysts to correlate by hand.
Licences are paid for capabilities that were never fully deployed.
The DAAKYI Approach
DAAKYI rationalizes the toolset, integrates technologies into shared workflows and connects telemetry to monitoring and ITSM.
Integrations are tested before go-live and documented for operations.
- 01
Tool rationalization review
- 02
Integration architecture
- 03
Deployment and configuration
- 04
Workflow and ITSM integration
In Depth
How the Discipline Works
Design Around Control Outcomes
Most security tools are bought to solve one problem and then left to run alone. A firewall logs to one console. An identity platform alerts in another. Endpoint tooling raises tickets nobody sees. Integration changes the unit of design from the product to the control outcome. Each tool becomes a source of events, a consumer of context, or an actor that can enforce a decision. When designers define those roles first, data flows have a purpose. Analysts see one timeline instead of several dashboards, and a decision made in one control can take effect in others without manual re-keying.
Normalize Telemetry Across Vendors
Every vendor describes events differently. One calls a field source address, another calls it client IP, and a third nests it inside a JSON object. Without normalization, correlation rules break or return noise. Integration work maps these fields to a common schema, applies consistent timestamps and time zones, and tags events with asset and identity context. Parsing quality decides detection quality. Teams also decide which events deserve forwarding, because shipping everything raises storage cost and buries signal. The result is telemetry that monitoring platforms and ITSM tools can act on without custom interpretation at every step.
Automate Response with Guardrails
Integrated tools can act, not just report. A confirmed malicious domain can be blocked at the secure web gateway and the firewall. A compromised account can be disabled and its sessions revoked. Automation of this kind needs guardrails. Designers set approval gates for high-impact actions, define rollback steps, and log every automated change for audit. Service workflows carry the human side: tickets are opened with evidence attached, routed to the right owner, and closed with a record. Done well, automation shortens the gap between detection and containment while keeping accountability clear.
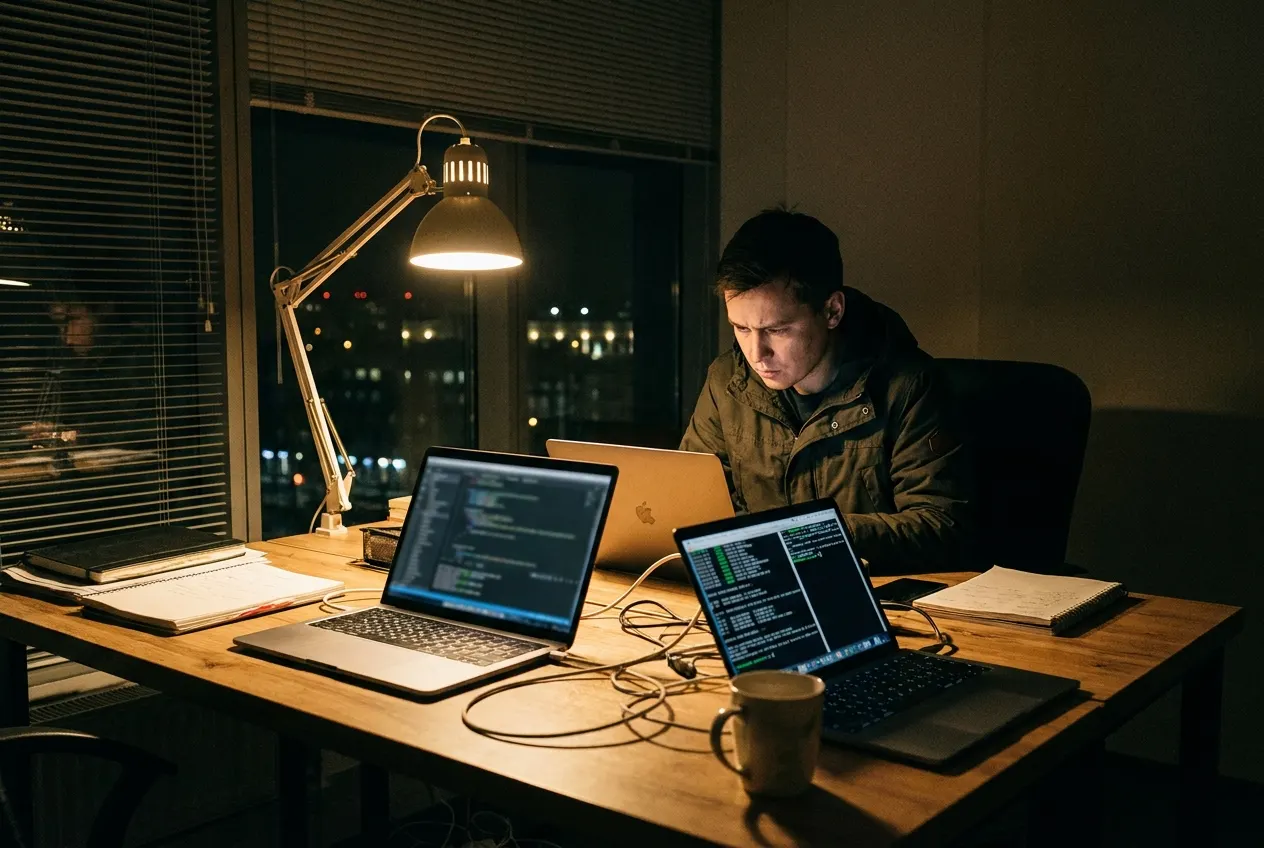
A security tool that cannot share what it sees is a license cost, not a control.
Capability Matrix
What the Service Includes
| Capability | Coverage | GUIDE | SECURE | OPERATE | Delivered Through |
|---|---|---|---|---|---|
| Infrastructure Integration | Design, deployment and support. | – | SECURE stage | – | Project Implementation |
| Telemetry Integration | Tools connected to monitoring. | – | SECURE stage | – | Project Implementation |
| Workflow and ITSM | Security tasks in service workflows. | – | SECURE stage | – | Project Implementation |
| Integrated Security Management | One governance, operations and reporting model. | – | SECURE stage | – | Project Implementation |
Infrastructure Integration
Design, deployment and support.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Telemetry Integration
Tools connected to monitoring.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Workflow and ITSM
Security tasks in service workflows.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Integrated Security Management
One governance, operations and reporting model.
- Stage
- SECURE
- Delivered Through
- Project Implementation
How It Works
How Security Technology Integration Works
- 01Rationalize
- 02Integrate
- 03Test
- 04Hand Over
Methodology
The Method, Step by Step
- 1
Inventory and Map
List every security tool, its licensed modules, its data sources and its owner. Map which capabilities overlap and which gaps remain. Record how events and tickets currently move between systems. This baseline shows where integration adds value and where retirement is the better choice than connection.
- 2
Design Data Flows
Define which tools send events, which receive context, and which enforce decisions. Choose the common schema, identity keys and time source. Specify connectors, authentication methods, volumes and failure behavior. Review the design against network segmentation and least privilege before any connector is built.
- 3
Build and Configure
Deploy missing capabilities and complete partial ones. Build connectors, parsers and automation playbooks in a non-production environment first. Apply configuration baselines so each tool enforces the intended policy. Keep changes under version control so every setting can be traced and reversed.
- 4
Test End to End
Replay sample events and run safe attack simulations to confirm each event arrives, parses correctly, triggers the right rule and opens the right ticket. Test failure cases such as expired credentials and dropped connections. Confirm that automated actions can be approved, logged and rolled back.
- 5
Document and Hand Over
Produce architecture diagrams, data-flow maps, runbooks and ownership tables. Train operators on normal behavior and common faults. Agree who monitors integration health and who approves changes. Hand over to the client team or continue support, with the same documentation either way.
Operating Model
Delivered from the SECURE Pillar
Pillar position
SECURE
Engineering, Architecture & Implementation
Engagement model
Project Implementation
Design and deployment of security technologies.
Best for · Modernization and transformation
Threat Scenarios
What It Looks Like in Practice
Related Alerts That Nobody Links
How It Shows Up
A phishing click appears in email logs, a suspicious login in identity logs, and an outbound connection in firewall logs. Each sits in a separate console.
Response
Shared identifiers and a common event schema let correlation join the three into one case with a single timeline.
Silent Connector Failure
How It Shows Up
A log connector stops after a certificate expires or an API token lapses, and the dashboard simply goes quiet.
Response
Health monitoring on each integration opens a ticket when expected event volume drops, and the runbook names the owner who fixes it.
Shelfware Modules
How It Shows Up
Licensed modules show no data, no policies, or only default configuration long after purchase.
Response
A rationalization review maps licensed features against actual use, then deploys what adds value and retires what overlaps.
Conflicting Enforcement Policies
How It Shows Up
Firewall, web gateway and endpoint rules allow or block the same traffic differently, which produces user complaints and repeated exceptions.
Response
Architecture assigns each control a clear enforcement role and aligns policy sources so an exception is made once.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Related Alerts That Nobody Links | A phishing click appears in email logs, a suspicious login in identity logs, and an outbound connection in firewall logs. Each sits in a separate console. | Shared identifiers and a common event schema let correlation join the three into one case with a single timeline. |
| Silent Connector Failure | A log connector stops after a certificate expires or an API token lapses, and the dashboard simply goes quiet. | Health monitoring on each integration opens a ticket when expected event volume drops, and the runbook names the owner who fixes it. |
| Shelfware Modules | Licensed modules show no data, no policies, or only default configuration long after purchase. | A rationalization review maps licensed features against actual use, then deploys what adds value and retires what overlaps. |
| Conflicting Enforcement Policies | Firewall, web gateway and endpoint rules allow or block the same traffic differently, which produces user complaints and repeated exceptions. | Architecture assigns each control a clear enforcement role and aligns policy sources so an exception is made once. |
Outcomes
What Your Institution Gains
- Controls integrated end to end
- More value from existing licences
- Every deployment tested
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Tool Inventory and Overlap Matrix | Shows what is licensed, what is used and where capabilities duplicate. |
| Integration Architecture Document | Defines each tool's role as event source, context consumer or enforcement point. |
| Data‑Flow and Field‑Mapping Specification | Records how events are transported, parsed and normalized. |
| Test Plan and Results | Proves each integration works, including failure and rollback cases. |
| Operations Runbook and Ownership Matrix | Tells operators how to monitor, troubleshoot and change each integration. |
| Role | Responsibility |
|---|---|
| CISO or Security Head (Client) | Sets the control outcomes the integrated estate must deliver and approves automation that changes production. |
| Security Architect (Provider) | Designs data flows, enforcement roles and the common schema across tools. |
| Integration Engineer (Provider) | Builds, tests and documents connectors, parsers and playbooks. |
| ITSM Service Owner (Client) | Defines how security tasks are routed, prioritized and closed inside service workflows. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Siloed
Each tool has its own console, owner and reports. Correlation happens by hand.
Stage 2
Connected
Key tools forward events to central monitoring. Parsing is inconsistent and some sources are missing.
Stage 3
Orchestrated
Normalized telemetry drives correlation, tickets and approved automated actions across controls.
Stage 4
Governed and Measured
Integration health, coverage and response outcomes are tracked, reviewed and tied to a single reporting model.
Frameworks and Regulation
The Standards That Shape This Work
NIST CSF 2.0
Integrated telemetry and workflows support the Detect and Respond functions, and shared reporting supports Govern. The framework has six functions: Govern, Identify, Protect, Detect, Respond and Recover.
ISO/IEC 27001:2022 Annex A
Annex A holds 93 controls in four themes, including technological controls such as logging and monitoring. Integration helps show those controls operate together, and ISO/IEC 27002:2022 gives implementation guidance.
PCI DSS v4.0.1
Logging and monitoring requirements depend on events from many systems reaching a place where they can be reviewed. Version 4.0's future-dated requirements became mandatory on March 31, 2025.
MITRE ATT&CK Enterprise
Its 14 tactics give a structure for testing whether integrated detections cover adversary behavior across tools, not just inside one product.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for a provider that reviews what you already own before recommending anything new.
- Look for integration designs that name the schema, identity keys and time source, not just a list of connectors.
- Look for test evidence that covers failure cases, not only the successful path.
- Look for handover documentation that your own team can operate without the original engineers.
Questions to ask a provider
- How do you identify overlapping tools and decide which to retire?
- How do you detect and alert on a silent integration failure?
- What guardrails apply to automated blocking and account disablement?
- What documentation and training do we receive at handover?
Regulatory & Industry Context
The Obligations This Service Supports
Integration supports evidence and monitoring requirements in ISO/IEC 27001, SOC 2 and PCI DSS.
Frameworks DAAKYI helps clients implement
- ISO/IEC 27001
- SOC 2
- PCI DSS
Framework references describe client implementation support, not DAAKYI certifications.
Technical Detail
For Architects and Security Leads
Telemetry sources and partner technologies
Technology partners DAAKYI works with in this area.
Framework and regulatory alignment
- ISO/IEC 27001
- SOC 2
- PCI DSS
Integration supports evidence and monitoring requirements in ISO/IEC 27001, SOC 2 and PCI DSS.
Architecture reference
How Security Technology Integration Works: Rationalize → Integrate → Test → Hand Over.
DAAKYI rationalizes the toolset, integrates technologies into shared workflows and connects telemetry to monitoring and ITSM.
Designing Log Pipelines That Survive Failure
Log transport choice shapes reliability. Syslog over UDP can drop events without any signal, so critical sources should use TCP with TLS or an agent that buffers to disk. Collectors should sit close to sources and forward over authenticated channels, which limits exposure of the central platform. Set a heartbeat for every source and alert when volume falls below a learned baseline. Parse at the collector or in a defined pipeline stage, and keep the raw event alongside the parsed one for forensics. Synchronize all sources to one time service, because skewed clocks break correlation and weaken evidence. Test queue behavior during an outage and confirm that backlog replays in order.
Securing the Integrations Themselves
Every integration is a new trust path. API tokens and service accounts that connect tools often hold broad rights and rarely rotate. Issue each connector its own credential with the minimum permissions it needs, store secrets in a vault, and set rotation and expiry alerts. Restrict connector traffic to known addresses and ports. Log every action a service account takes, especially automated blocks and account disablement. Review these accounts as privileged identities, because an attacker who captures one can silence detections or push harmful policy changes across several controls at once. Include integrations in change management and periodic access review.
Glossary
Key Terms
- Normalization
- Converting events from different vendors into one consistent field structure so they can be correlated.
- Connector
- A configured link, such as an API integration or log forwarder, that moves data or commands between two tools.
- Playbook
- A defined sequence of automated and manual steps that runs when a specific detection or ticket occurs.
- Shelfware
- Licensed security capability that was purchased but never fully deployed or used.
Related
Explore Connected Capabilities
Related services
Solutions
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
Technology partners
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About Security Technology Integration
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.

Next Step
Discuss Security Technology Integration with DAAKYI
Tell us about your environment and obligations. A DAAKYI specialist for Security Technology Integration will respond.
Talk to a Cybersecurity Expert