
SECURE · Cybersecurity Architecture & Engineering
Security Designed into the Architecture, Not Bolted On.
We design and engineer security architectures that fit your environment, obligations and growth plans.
- Zero Trust, resilient architectures
- Controls integrated end to end
- Faster, safer project delivery
- 1Establish Scope and Drivers
- 2Model Threats and Gaps
- 3Draft Reference Patterns
- 4Build and Harden
- 5Test and Govern
Executive Summary
- 01Security architecture defines how identity, network, data and monitoring controls work together as one system.
- 02Reusable reference patterns let project teams build securely without waiting for case-by-case advice.
- 03Validated configurations and drift monitoring keep the design accurate after deployment.
The Challenge
Security estates grow through acquisitions, projects and urgent fixes until no one can describe how the pieces fit.
Gaps open between tools, and new systems go live without an agreed security design.
The DAAKYI Approach
DAAKYI reviews the current architecture, defines target‑state security patterns and engineers controls so they work together.
Designs are documented as reference architectures your teams can reuse.
- 01
Current-state architecture review
- 02
Target-state security architecture
- 03
Reference patterns and standards
- 04
Engineering and controls hardening
In Depth
How the Discipline Works
Start with How the Estate Really Works
Architecture work begins with evidence, not diagrams. Engineers collect network maps, identity stores, cloud account structures, data flows and the security tools already deployed. They then compare the documented picture with what interviews and configuration exports reveal. The differences matter most. An undocumented trust path between a vendor network and a production database, or a service account with standing administrative rights, will not appear in an inventory. Mapping these facts to business services shows which assets carry the most risk. The result is a current-state baseline that every later design decision can be tested against, and that leaders can read without a security background.
Design Patterns Around Trust Boundaries
A target-state design defines where trust changes and what must be proven at each crossing. Identity, network segmentation, data protection, logging and endpoint control are treated as one system rather than separate products. Each pattern states its purpose, its components, the threats it addresses and the assumptions it relies on. NIST SP 800-207 gives a vocabulary for this thinking, including policy decision and enforcement points. Patterns also record trade-offs, such as the latency cost of inspection or the operational load of tight segmentation. Written this way, a pattern can be reviewed, challenged and reused, instead of living in one engineer's memory.
Engineering Turns Design into Enforced Controls
A design only protects anything once it is configured, deployed and monitored. Engineering translates each pattern into hardened baselines, infrastructure-as-code modules, policy definitions and logging requirements. Published hardening guidance, including the CIS Critical Security Controls v8, helps set the baseline. Changes pass through testing before reaching production, and drift detection shows when a setting moves away from standard. Validation then checks that controls behave as intended, for example by confirming that a blocked path is actually blocked and that an alert reaches the people who must act on it. Evidence from these tests feeds audits and future design reviews.
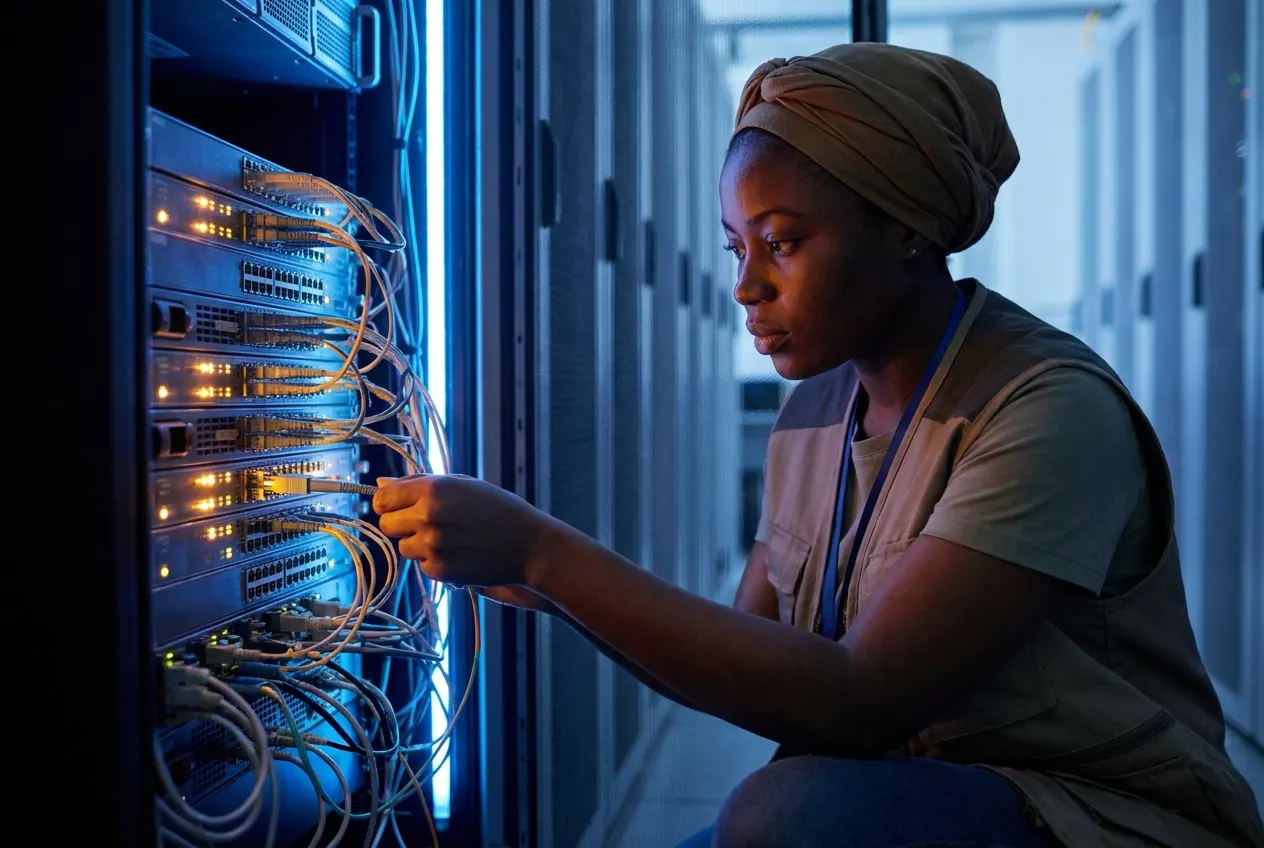
A security architecture is tested not by how it looks on a diagram, but by what an attacker cannot reach.
Capability Matrix
What the Service Includes
| Capability | Coverage | GUIDE | SECURE | OPERATE | Delivered Through |
|---|---|---|---|---|---|
| Security Architecture Design | Target-state patterns across domains. | – | SECURE stage | – | Project Implementation |
| Controls Engineering and Hardening | Configurations engineered to standard. | – | SECURE stage | – | Project Implementation |
| Design Authority Support | Security review of new projects. | – | SECURE stage | – | Project Implementation |
| Architecture Documentation | Reusable reference architectures. | – | SECURE stage | – | Project Implementation |
Security Architecture Design
Target-state patterns across domains.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Controls Engineering and Hardening
Configurations engineered to standard.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Design Authority Support
Security review of new projects.
- Stage
- SECURE
- Delivered Through
- Project Implementation
Architecture Documentation
Reusable reference architectures.
- Stage
- SECURE
- Delivered Through
- Project Implementation
How It Works
How Cybersecurity Architecture & Engineering Works
- 01Review
- 02Design
- 03Engineer
- 04Validate
Methodology
The Method, Step by Step
- 1
Establish Scope and Drivers
Define the business services, regulatory obligations, risk appetite and planned changes that the architecture must support. Confirm which standards apply, such as ISO/IEC 27001 or PCI DSS, and who owns each decision. This step prevents elegant designs that solve the wrong problem and sets measurable design principles for later review.
- 2
Model Threats and Gaps
Analyze how realistic adversaries would attack the current estate, using MITRE ATT&CK tactics as a shared language. Compare existing controls with the target requirements and rank gaps by likelihood and impact. The output is a prioritized list of weaknesses tied to specific business services, not a generic findings catalog.
- 3
Draft Reference Patterns
Produce patterns for identity, network, data, workload and monitoring domains. Each one includes a diagram, control requirements, approved technologies and known exceptions. Stakeholders from infrastructure, application and risk teams review drafts so that patterns are workable before any build begins, and ownership of each pattern is assigned.
- 4
Build and Harden
Implement the patterns in sequence, starting with the foundations other controls depend on, usually identity and logging. Apply hardened baselines, automate configuration where possible and test each change in a non-production environment. Record every deviation from the pattern with a reason and an owner.
- 5
Test and Govern
Verify that controls work through configuration review, functional testing and attack simulation against the design assumptions. Then set up design review gates for new projects, and schedule pattern reviews as technology and threats change. Governance keeps the architecture accurate after the original build team has moved on.
Operating Model
Delivered from the SECURE Pillar
Pillar position
SECURE
Engineering, Architecture & Implementation
Engagement model
Project Implementation
Design and deployment of security technologies.
Best for · Modernization and transformation
Threat Scenarios
What It Looks Like in Practice
Lateral Movement Across a Flat Network
How It Shows Up
An intruder who compromises one workstation reaches servers, backups and management interfaces with little friction.
Response
Segmentation patterns separate user, server, management and backup zones. Rules between zones are enforced and logged, and exceptions are reviewed.
Overprivileged Identities
How It Shows Up
Service accounts and administrators hold standing access far beyond their tasks, and no one can produce a complete list.
Response
Identity architecture introduces least privilege, just-in-time elevation and tiered administration, with privileged activity logged centrally.
Unreviewed Cloud Deployment
How It Shows Up
A project team launches a workload with public storage or permissive security groups because no design standard existed.
Response
A design authority reviews new projects against reference architectures, and guardrails in code block known unsafe configurations.
Tool Sprawl with Detection Blind Spots
How It Shows Up
Several products raise alerts, yet an attacker technique described in MITRE ATT&CK goes unseen because no tool owns that telemetry.
Response
Engineers map detection coverage against ATT&CK tactics, identify missing log sources and feed telemetry into one monitoring pipeline.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Lateral Movement Across a Flat Network | An intruder who compromises one workstation reaches servers, backups and management interfaces with little friction. | Segmentation patterns separate user, server, management and backup zones. Rules between zones are enforced and logged, and exceptions are reviewed. |
| Overprivileged Identities | Service accounts and administrators hold standing access far beyond their tasks, and no one can produce a complete list. | Identity architecture introduces least privilege, just-in-time elevation and tiered administration, with privileged activity logged centrally. |
| Unreviewed Cloud Deployment | A project team launches a workload with public storage or permissive security groups because no design standard existed. | A design authority reviews new projects against reference architectures, and guardrails in code block known unsafe configurations. |
| Tool Sprawl with Detection Blind Spots | Several products raise alerts, yet an attacker technique described in MITRE ATT&CK goes unseen because no tool owns that telemetry. | Engineers map detection coverage against ATT&CK tactics, identify missing log sources and feed telemetry into one monitoring pipeline. |
Outcomes
What Your Institution Gains
- Zero Trust, resilient architectures
- Controls integrated end to end
- Faster, safer project delivery
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Current‑State Architecture Assessment | Records actual trust paths, controls and gaps so decisions rest on evidence. |
| Target‑State Security Architecture | Describes the intended design across identity, network, data, workload and monitoring domains. |
| Reference Pattern Library | Gives project teams approved, reusable designs for common situations. |
| Hardening Baselines and Configuration Standards | Define the exact settings each platform must meet. |
| Control Validation Report | Shows which controls were tested, by what method and with what result. |
| Role | Responsibility |
|---|---|
| Chief Information Security Officer (Client) | Owns risk appetite and approves the target-state design and any exceptions to it. |
| Security Architect (Provider or Client) | Authors the patterns and keeps them consistent across domains. |
| Security Engineer (Provider) | Builds, configures and tests controls to the agreed baseline. |
| Platform or Project Owner (Client) | Brings new systems to design review and operates the resulting controls. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Ad Hoc
Controls come from individual projects and urgent fixes. No shared design exists, and exceptions are not recorded.
Stage 2
Documented
Standards and diagrams exist, but projects apply them unevenly and configuration drift goes unnoticed.
Stage 3
Governed
Reference patterns are mandatory, design reviews gate new projects, and deviations are tracked with named owners.
Stage 4
Measured
Controls are deployed as code and tested continuously. Coverage against threats and obligations is measured and drives design updates.
Frameworks and Regulation
The Standards That Shape This Work
NIST CSF 2.0
Its six functions (Govern, Identify, Protect, Detect, Respond, Recover) let reviewers check that an architecture covers more than prevention. The Govern function suits design authority and risk ownership.
ISO/IEC 27001:2022
Annex A lists 93 controls divided into four themes: organizational, people, physical, and technological. Architecture primarily supplies evidence for the technological theme, and ISO/IEC 27002:2022 provides guidance on implementing those controls.
NIST SP 800-207
It defines Zero Trust Architecture concepts, supporting designs that verify each access request rather than trusting network location.
PCI DSS v4.0.1
Scoping and segmentation decisions shape the cardholder data environment. The future-dated requirements of v4.0 became mandatory on 31 March 2025.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for a provider that begins with your existing estate and can explain which tools to keep and why.
- Expect patterns written at a level your engineers can implement, not slideware.
- Ask for evidence that designs are tested after deployment, not only signed off on paper.
- Confirm that documentation and training leave your team able to extend the architecture alone.
Questions to ask a provider
- How do you decide which of our existing controls to retain?
- Can you show a sample reference pattern with its threats and assumptions?
- How do you detect configuration drift after handover?
- Which standards do you map designs to, and how is that mapping evidenced?
Regulatory & Industry Context
The Obligations This Service Supports
Architectures align to NIST CSF, ISO/IEC 27001 and CIS Controls, and reflect sector requirements such as PCI DSS.
Frameworks DAAKYI helps clients implement
- NIST CSF
- ISO/IEC 27001
- CIS Controls
- PCI DSS
Framework references describe client implementation support, not DAAKYI certifications.
Technical Detail
For Architects and Security Leads
Framework and regulatory alignment
- NIST CSF
- ISO/IEC 27001
- CIS Controls
- PCI DSS
Architectures align to NIST CSF, ISO/IEC 27001 and CIS Controls, and reflect sector requirements such as PCI DSS.
Architecture reference
How Cybersecurity Architecture & Engineering Works: Review → Design → Engineer → Validate.
DAAKYI reviews the current architecture, defines target-state security patterns and engineers controls so they work together.
Segmentation and Policy Enforcement Design
Effective segmentation starts with data flows, not VLANs. Engineers classify workloads by sensitivity and function, then define allowed flows between zones as explicit rules with named owners. Enforcement can sit at network firewalls, host-based firewalls, cloud security groups or service mesh policy, and the pattern states which layer is authoritative. Management planes receive their own zone with strong authentication and session logging. East-west traffic is logged at enforcement points so detection teams can see lateral movement attempts. Rule sets are stored as code, reviewed through pull requests and tested against expected-deny cases. Periodic rule recertification removes stale exceptions, which otherwise accumulate and quietly erase the intended boundaries.
Identity as the Control Plane
In hybrid and cloud estates, identity is the most contested control point. The architecture defines authoritative identity sources, federation paths and how workloads authenticate without embedded secrets. Administrative access follows tiering: separate accounts, privileged access workstations or equivalent controls, and just-in-time elevation with approval and recording. Conditional access policies evaluate user, device and risk signals before granting access to sensitive applications. Service accounts are inventoried, scoped and rotated, with ownership assigned. Identity logs flow to the monitoring platform, where detections look for impossible travel, token misuse and unusual privilege changes. Break-glass accounts are protected, tested and alarmed so emergency access remains possible without becoming a standing weakness.
Glossary
Key Terms
- Reference Architecture
- A vetted, reusable design showing the components, controls and relationships for a common use case.
- Trust Boundary
- A point where data or requests move between zones of different trust and must be verified.
- Design Authority
- A group that reviews and approves security-relevant designs before they are built.
- Configuration Drift
- The gradual divergence of a system's live settings from its approved baseline.
Related
Explore Connected Capabilities
Related services
Solutions
Platforms
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About Cybersecurity Architecture & Engineering
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.

Next Step
Discuss Cybersecurity Architecture & Engineering with DAAKYI
Tell us about your environment and obligations. A DAAKYI specialist for Cybersecurity Architecture & Engineering will respond.
Talk to a Cybersecurity Expert