
SECURE · Zero Trust Architecture
Verify Every User, Device and Connection, Every Time.
We move you from perimeter trust to identity-centric, segmented access that limits how far an intruder can move.
- Zero Trust, resilient architectures
- Reduced lateral movement
- Secure access from anywhere
- 1Define Protect Surfaces
- 2Map Transaction Flows
- 3Design Access Policy
- 4Enforce in Phases
- 5Monitor and Tune
Executive Summary
- 01Zero Trust replaces location-based trust with a decision made on every request, using identity, device state and context.
- 02Value comes from shrinking what a stolen credential can reach, not from buying a single product.
- 03Progress is measured by protect surfaces enforced, flows mapped and exceptions retired.
The Challenge
Remote work, cloud services and third‑party access have dissolved the network perimeter.
Flat networks and implicit trust let a single stolen credential reach critical systems.
The DAAKYI Approach
DAAKYI defines protect surfaces, maps transaction flows and designs policies that enforce least‑privilege access for users, devices and workloads.
Implementation is phased so each step reduces risk without disrupting operations.
- 01
Protect-surface definition
- 02
Identity and device trust policies
- 03
Segmentation and secure access design
- 04
Phased implementation roadmap
In Depth
How the Discipline Works
No Implicit Trust by Location
Zero Trust starts from an assumption: no network location is trustworthy by default. An office address, a VPN connection or a position inside the data center no longer proves anything. The policy engine considers who is asking, what device they are using, what they want to reach and how risky the context looks. Access is granted only to the specific resource, only for that session, and only at the level the task requires. NIST SP 800-207 describes this as separating the decision point from the enforcement point, so policy stays consistent regardless of where users or workloads sit.
Identity and Device as Controls
Identity is the new control plane. Strong authentication, ideally phishing-resistant, establishes who the user is. Device posture establishes whether the endpoint is managed, patched and free of known compromise indicators. Workloads and service accounts need the same rigor, because machine identities often outnumber human ones and are rarely reviewed. Conditional rules combine these signals. A finance analyst on a managed laptop may reach the ledger application, while the same analyst on an unmanaged tablet receives read-only access to email. When posture degrades mid-session, access is reduced or revoked rather than waiting for the next login.
Segmentation and Continuous Monitoring
Segmentation limits the damage when prevention fails. Instead of one flat network, systems are grouped around protect surfaces: the data, applications, assets and services that matter most. Traffic between groups passes through enforcement points that permit only mapped, necessary flows. An intruder who captures one credential then finds few reachable targets. Monitoring closes the loop. Logs from identity, endpoint, network and application layers feed detection, and unexpected flows become signals worth investigating. Policy is then tuned from evidence, tightening rules that are too broad and relaxing those that break legitimate work.
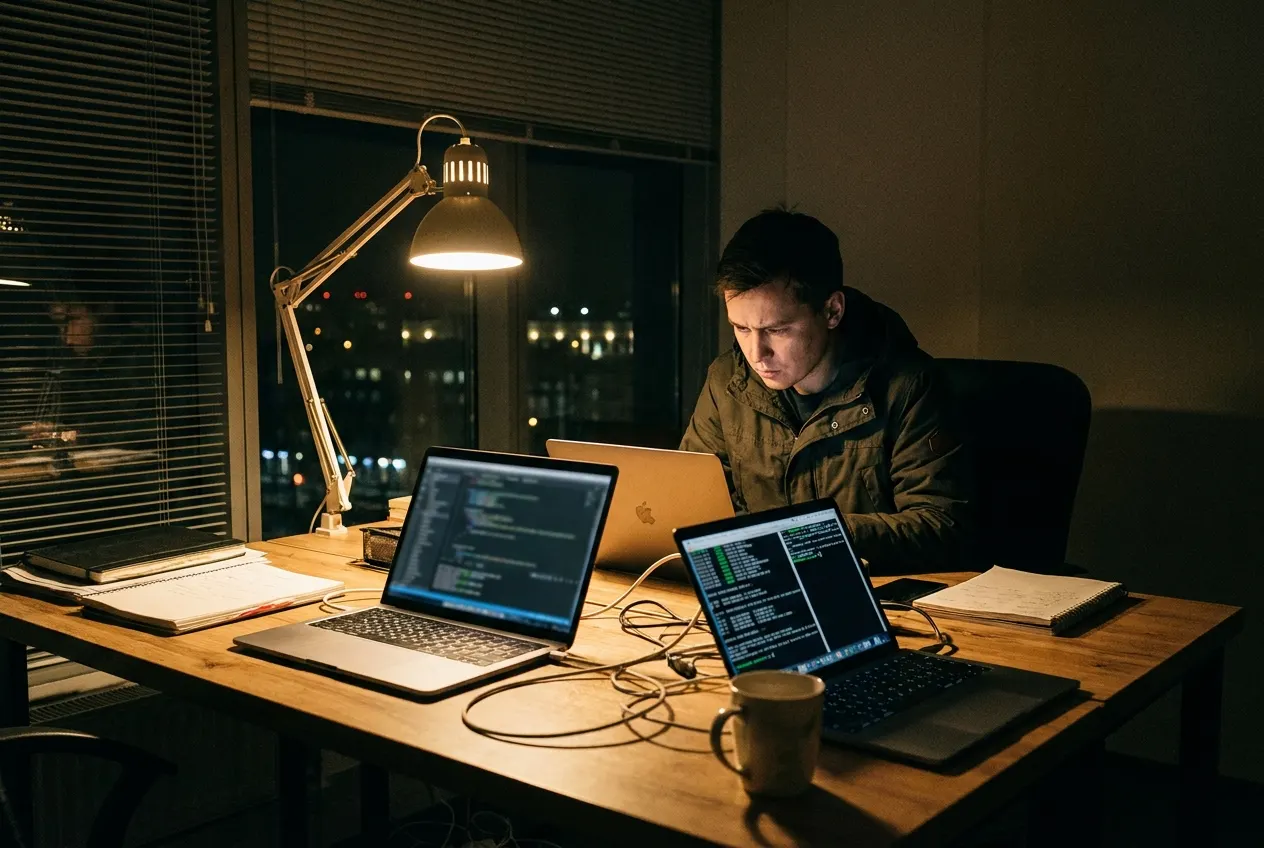
A stolen password should open one door, not the whole building.
Capability Matrix
What the Service Includes
| Capability | Coverage | GUIDE | SECURE | OPERATE | Delivered Through |
|---|---|---|---|---|---|
| Zero Trust Strategy | Principles and phased roadmap. | – | SECURE stage | – | Project Implementation, Advisory Engagements |
| Secure Access (SSE) | Policy-based access to applications. | – | SECURE stage | – | Project Implementation, Advisory Engagements |
| Micro‑Segmentation | Limits on lateral movement. | – | SECURE stage | – | Project Implementation, Advisory Engagements |
| Continuous Verification | Identity and device posture checks. | – | SECURE stage | – | Project Implementation, Advisory Engagements |
Zero Trust Strategy
Principles and phased roadmap.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Advisory Engagements
Secure Access (SSE)
Policy-based access to applications.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Advisory Engagements
Micro‑Segmentation
Limits on lateral movement.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Advisory Engagements
Continuous Verification
Identity and device posture checks.
- Stage
- SECURE
- Delivered Through
- Project Implementation, Advisory Engagements
How It Works
How Zero Trust Architecture Works
- 01Define
- 02Map Flows
- 03Enforce
- 04Monitor
Methodology
The Method, Step by Step
- 1
Define Protect Surfaces
Identify the data, applications, assets and services whose compromise would hurt most. Keep the list small enough to protect well. Rank each by business impact and regulatory exposure, and record the owner. Starting narrow gives early wins and prevents the program from stalling under the weight of the entire estate.
- 2
Map Transaction Flows
Document how users, devices, applications and data actually interact with each protect surface. Use traffic captures, access logs and owner interviews rather than diagrams alone. The result shows which flows are legitimate, which are legacy habits, and which dependencies would break if blocked, so policy can be precise.
- 3
Design Access Policy
Write rules in plain language first: who, from which device state, to which resource, for what purpose. Translate them into identity provider conditions, network controls and application permissions. Define exceptions explicitly with owners and expiry dates. Review the draft with business owners so security rules match how work is really done.
- 4
Enforce in Phases
Apply controls one protect surface at a time. Begin in monitor-only mode to see what would be blocked, then move to enforcement once false positives are understood. Prepare rollback procedures and user communication in advance. Each phase should reduce measurable exposure without surprising the people who depend on the systems.
- 5
Monitor and Tune
Collect telemetry on authentication, device posture, policy decisions and denied connections. Review denials for both attacks and broken workflows. Test controls by simulating credential theft and lateral movement, using MITRE ATT&CK tactics as a guide. Feed findings back into policy so the architecture improves with each cycle.
Operating Model
Delivered from the SECURE Pillar
Pillar position
SECURE
Engineering, Architecture & Implementation
Engagement model
Project Implementation
Design and deployment of security technologies.
Best for · Modernization and transformation
Engagement model
Advisory Engagements
Fixed-scope assessments, strategy, compliance and testing.
Best for · Defined questions with a clear deliverable
Threat Scenarios
What It Looks Like in Practice
Phished Credentials
How It Shows Up
A valid login appears from an unfamiliar device or location, followed by access to systems the user never touches.
Response
Device posture and context checks deny or step up authentication, and segmentation keeps the session away from unrelated protect surfaces.
Compromised Vendor Account
How It Shows Up
A supplier login reaches internal file shares or administrative interfaces beyond the maintenance task it was issued for.
Response
Third-party access is limited to named applications, time-bound and brokered, so the vendor never sits on the internal network.
Ransomware Spreading Between Servers
How It Shows Up
Workstations or servers begin connecting to peers over SMB, RDP or SSH that they have never used before.
Response
Micro-segmentation blocks peer-to-peer administrative protocols by default, and denied connections raise an alert for investigation.
Over‑Privileged Service Account
How It Shows Up
A service account with broad rights authenticates interactively or from a host outside its normal pattern.
Response
Workload identities are scoped to specific flows, reviewed regularly and monitored for deviation from their baseline.
| Scenario | How It Shows Up | Response |
|---|---|---|
| Phished Credentials | A valid login appears from an unfamiliar device or location, followed by access to systems the user never touches. | Device posture and context checks deny or step up authentication, and segmentation keeps the session away from unrelated protect surfaces. |
| Compromised Vendor Account | A supplier login reaches internal file shares or administrative interfaces beyond the maintenance task it was issued for. | Third-party access is limited to named applications, time-bound and brokered, so the vendor never sits on the internal network. |
| Ransomware Spreading Between Servers | Workstations or servers begin connecting to peers over SMB, RDP or SSH that they have never used before. | Micro-segmentation blocks peer-to-peer administrative protocols by default, and denied connections raise an alert for investigation. |
| Over‑Privileged Service Account | A service account with broad rights authenticates interactively or from a host outside its normal pattern. | Workload identities are scoped to specific flows, reviewed regularly and monitored for deviation from their baseline. |
Outcomes
What Your Institution Gains
- Zero Trust, resilient architectures
- Reduced lateral movement
- Secure access from anywhere
Deliverables and Roles
What You Receive, and Who Does What
| Deliverable | Purpose |
|---|---|
| Protect‑Surface Register | Lists each protect surface with its owner, sensitivity and business impact so priorities are explicit. |
| Transaction Flow Maps | Show the verified paths between users, devices, applications and data that policy must permit. |
| Access Policy Matrix | Defines who may reach what, under which identity and device conditions. |
| Segmentation Design | Specifies zones, enforcement points and allowed traffic between them. |
| Exception and Rollback Register | Tracks approved deviations with owners and expiry dates, plus the steps to reverse each change. |
| Role | Responsibility |
|---|---|
| Chief Information Security Officer (Client) | Sponsors the program, sets risk appetite and arbitrates between security rules and business needs. |
| Application Owner (Client) | Confirms legitimate flows and approves the access rules for the systems they run. |
| Identity and Access Lead (Client) | Maintains authentication strength, lifecycle processes and privileged account controls. |
| Security Architect (Provider) | Translates protect surfaces and flows into enforceable policy, segmentation and control designs. |
Maturity Model
Where Organizations Typically Stand
Stage 1
Perimeter‑Centric
Trust is granted by network location, internal networks are flat and remote access relies on broad VPN connectivity.
Stage 2
Identity‑Aware
Strong authentication and device checks gate access to key applications, but internal traffic remains largely open.
Stage 3
Segmented
Protect surfaces are isolated, flows are mapped and only necessary connections are allowed between zones.
Stage 4
Adaptive
Policy responds to live risk signals, access is revoked as posture changes and results are tested against adversary techniques.
Frameworks and Regulation
The Standards That Shape This Work
NIST SP 800-207
Defines Zero Trust Architecture concepts, including the policy engine, policy administrator and enforcement point. It provides a vendor-neutral vocabulary for design and procurement discussions.
NIST CSF 2.0
Its six functions (Govern, Identify, Protect, Detect, Respond, Recover) frame Zero Trust outcomes. Access control and segmentation sit mainly under Protect, while monitoring supports Detect.
ISO/IEC 27001:2022
Annex A technological controls cover access rights, secure authentication and network segregation. ISO/IEC 27002:2022 gives implementation guidance for them.
PCI DSS v4.0.1
Segmentation is not mandated, but validated segmentation can reduce the scope of the cardholder data environment. Access control and authentication requirements apply within it.
Buyer Guidance
Choosing the Right Provider
What to look for
- Look for a provider that begins with protect surfaces and business flows, not with a product catalog.
- Look for designs that cover workloads and service accounts, not only employee logins.
- Look for a plan that includes monitor-only stages, rollback steps and user communication.
- Look for clear treatment of legacy systems, with compensating controls where agents or modern authentication cannot be used.
Questions to ask a provider
- How do you decide which protect surfaces come first, and who signs off?
- How will you discover flows we have never documented?
- What happens to applications that cannot support modern authentication?
- How will we know, with evidence, that lateral movement has been reduced?
Regulatory & Industry Context
The Obligations This Service Supports
Designs follow NIST CSF and ISO/IEC 27001 control objectives and support access-control requirements in PCI DSS.
Frameworks DAAKYI helps clients implement
- NIST CSF
- ISO/IEC 27001
- PCI DSS
Framework references describe client implementation support, not DAAKYI certifications.
Technical Detail
For Architects and Security Leads
Telemetry sources and partner technologies
Technology partners DAAKYI works with in this area.
Framework and regulatory alignment
- NIST CSF
- ISO/IEC 27001
- PCI DSS
Designs follow NIST CSF and ISO/IEC 27001 control objectives and support access-control requirements in PCI DSS.
Architecture reference
How Zero Trust Architecture Works: Define → Map Flows → Enforce → Monitor.
DAAKYI defines protect surfaces, maps transaction flows and designs policies that enforce least-privilege access for users, devices and workloads.
Decision and Enforcement Architecture
NIST SP 800-207 defines a policy engine, a policy administrator and a policy enforcement point. The engine decides, the administrator establishes or tears down the session path, and the enforcement point carries the traffic. Inputs include identity provider assertions, device compliance state, threat intelligence, activity logs and data access policy. Deployment variants include agent and gateway models, enclave gateways and resource portals. Selection depends on whether workloads are managed, whether legacy protocols must be supported and where latency matters. A common failure is granting trust based on network location instead of the authenticated decision. Another is leaving direct paths to applications open, which lets attackers bypass the broker entirely.
Micro-Segmentation Techniques
Micro-segmentation can be implemented in the network, the hypervisor, the host or the identity layer. Host-based agents enforce rules per workload and follow the workload across data centers and clouds. Network-based approaches use firewalls and virtual routing, and suit environments where agents cannot be installed, such as legacy or operational technology systems. Rules should be built from observed flows, then expressed by labels such as application, environment and sensitivity rather than IP addresses. This keeps policy stable as workloads scale. Prioritize blocking administrative protocols like RDP, SMB and SSH between peers, since adversaries rely on them for lateral movement.
Glossary
Key Terms
- Protect Surface
- The small set of critical data, applications, assets and services that a Zero Trust design is built to defend.
- Policy Enforcement Point
- The component that permits, blocks or terminates a connection based on the policy engine's decision.
- Lateral Movement
- An intruder's progression from an initial foothold to other systems inside the environment.
- Device Posture
- The measured security state of an endpoint, such as management status, patch level and protection health.
Related
Explore Connected Capabilities
Related services
Solutions
Platforms
Proof Points
What We Can Stand Behind
- Every stage of DAAKYI's delivery methodology produces documented, auditable deliverables.
Technology partners
FAQ
Questions Leaders Ask

DAAKYI Intelligence
Ask Kasara About Zero Trust Architecture
Kasara, our AI assistant, answers from DAAKYI's published content and can connect you with a specialist.

Next Step
Discuss Zero Trust Architecture with DAAKYI
Tell us about your environment and obligations. A DAAKYI specialist for Zero Trust Architecture will respond.
Talk to a Cybersecurity Expert